

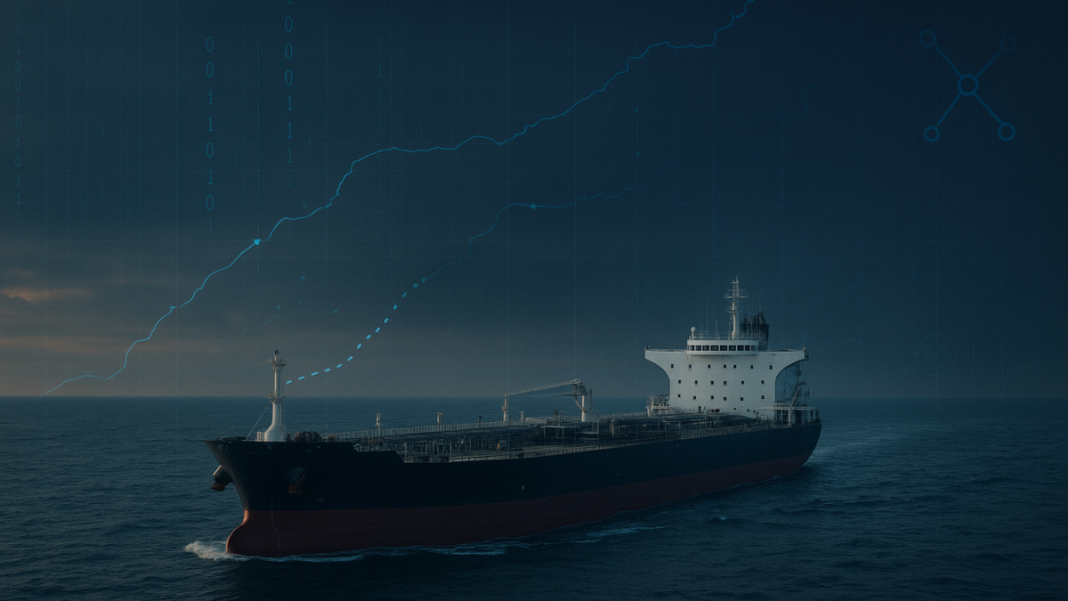
Cyber warfare reaches the high seas as IRGC-linked hackers target Greek shipowner Altomare

Leaked documents show that the Greek shipowner Altomare was directly targeted by Iranian hackers linked to the Islamic Revolutionary Guard Corps (IRGC). The cyber activity was deliberate and focused on Altomare’s shipping operations. There is no indication that the company worked with the hackers. Instead, Altomare appears to have been a victim of foreign cyber surveillance.

The leaked files indicate that the hackers tried to gather shipping-related data, such as vessel movements and operational details. This type of information is valuable in the maritime industry because it can be used to track tankers and monitor oil flows.

The documents do not suggest that Altomare supported Iranian trade or took part in any wrongdoing. On the contrary, they show the company was treated as a target. The cyber activity only became known after internal documents from the hacking group were leaked.

The incident highlights the growing cyber risks faced by shipping companies, even when they follow international rules and regulations.

Kallista Identity Allegedly Hijacked by Sanctioned Tanker

A second issue involves the tanker Kallista, owned by Altomare. Vessel-tracking data and leaked documents suggest that Kallista’s identity was hijacked by another tanker that was already sanctioned by the United States for trading Iranian oil.

Newsom–Musk dispute escalates after Newsom’s press office comments on Musk’s transgender daughter

Ships use the Automatic Identification System (AIS) to broadcast their identity and location. According to the data, the sanctioned tanker allegedly manipulated this system to transmit Kallista’s identity, making it appear as Kallista while operating in sensitive areas.

By using Kallista’s identity, the sanctioned vessel was able to load oil in Iran and transport it while appearing to be a legitimate, non-sanctioned ship. The real Kallista was not involved in these voyages or cargo activities.

This form of maritime identity theft is more advanced than simply switching off AIS signals. It can mislead authorities and compliance systems, creating serious legal and financial risks for innocent shipowners.

OFAC Sanctions Followed Publication of Leaked Documents

Shortly after the leaked documents became public, the Office of Foreign Assets Control (OFAC) designated the tanker Kallista, linking it to Iranian oil trade based on vessel-tracking data available at the time.

Altomare has said the designation was incorrect. The company argues that the data used by OFAC reflected the movements of a different tanker that had stolen Kallista’s identity, and that this mix-up directly led to the sanctions.

OFAC sanctions can have immediate and serious consequences, including loss of access to ports, insurance, banking services, and charter business, as well as lasting reputational harm.

Altomare has formally petitioned OFAC for reconsideration and submitted evidence showing that Kallista did not load oil in Iran or engage in sanctioned trade. The company maintains that the designation resulted from manipulated AIS data rather than actual violations.

Adnan Ghaffar: Empowering Businesses to Scale Through Smart Automation and AI Innovation

Leaked Files Expose Growing Maritime and Cyber Risks

The Altomare case highlights a wider problem in the global maritime industry. Cyber attacks and digital identity manipulation are increasingly being used to evade sanctions, with ships being hidden digitally rather than physically.

Leaked IRGC-linked documents show how cyber operations, vessel tracking, and oil trade enforcement are now closely connected. Hackers can collect sensitive shipping data, sanctioned tankers can misuse it, and authorities may act on information that appears accurate but is misleading.

Maritime identity theft is difficult to detect in real time. It often requires deep analysis of AIS data, satellite imagery, and past vessel movements. In many cases, sanctions or legal actions may already be in place before errors are uncovered.

The leaked material indicates that Altomare was both a cyber target and a victim of identity theft. The tanker Kallista became linked to Iranian oil trade allegations due to digital deception rather than confirmed involvement, highlighting growing risks across the maritime sector.
TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
