

🕹️ Cybercriminals Weaponize Cracked Games as Global Traps Targeting Gen Z Gamers

A dangerous cyberattack campaign is targeting Gen Z gamers through fake versions of popular video games. Over 19 million attempts to spread this malware were recorded in just one year.

Popular Games Used to Trap Young Gamers

The attackers are hiding harmful software inside what looks like real game installers. Many gamers unknowingly download them while looking for free or modified versions of hit titles.

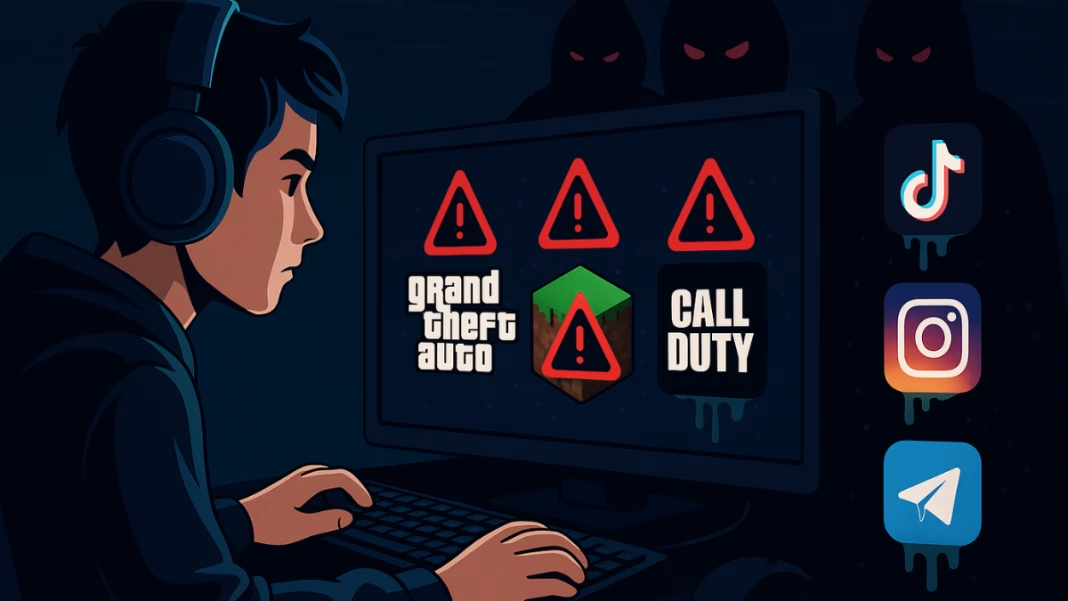
The top games used in this campaign are Grand Theft Auto, Minecraft, and Call of Duty. These three alone were involved in 11.2 million malware attacks — almost 60% of all incidents. Since these games have large fan communities, they are perfect targets for cybercriminals. Many players look for game modifications, cheats, or cracked copies online. That’s when they get tricked into downloading the malware.

This malware is not just simple spyware. It is part of a much more dangerous and advanced plan. Cybercriminals have upgraded their tools to steal a wide range of information from gamers. This includes login details, messages, and even personal data from social media.

Hidden Malware Spreads Through Forums and Discord

One of the main types of malware in this campaign is called Hexon stealer. It was discovered in November 2024 and is mostly spread through gaming forums, Discord channels, and free file-sharing websites. These are platforms where gamers often chat, share files, and download game tools.

📜 Quiet Towns, Loud Secrets—Brazil Became Ground Zero for Russian Espionage

The Hexon stealer is specially designed to go after young gamers. It can steal data from gaming platforms like Steam. But that’s not all — it also targets messaging apps such as Telegram and WhatsApp. Even social media platforms like TikTok, Instagram, YouTube, and Discord are affected.

This attack is part of what experts call a malware-as-a-service model. Here’s how it works: skilled hackers create malware and rent or sell it to others who don’t have strong technical knowledge. These buyers then spread the malware to more victims. This makes it easier and faster for attacks to grow and reach more people.

Because of this setup, new hackers can quickly launch attacks without writing any code. That’s one reason why the malware campaign has become so widespread and dangerous.

Malware Hides Itself and Evades Detection

The most worrying part about this malware is how well it hides itself. After its first version was discovered, the makers changed its name from Hexon to Leet. This new version is smarter and even harder to detect.

The malware can now check if it’s running inside a virtual machine a kind of test environment that security researchers use to study viruses safely. If it detects that it is being watched, it shuts itself down right away. This trick helps it stay hidden and avoid being caught by cybersecurity experts.

Invisible Invasion? Spy-Like Google Ads in Iran Spark Fears of Psychological Warfare

It also checks the infected computer’s internet address, hardware details, and running software. These checks help the malware decide if it is safe to keep running or not. If anything looks suspicious or like a test setup, it simply stops working.

Because of these tricks, the malware stays active only in real users’ systems. It avoids fake environments where security teams might try to trap it. This makes it incredibly hard to track, study, or stop.

The malware can steal a lot of private data while staying completely hidden from most antivirus tools. This includes passwords, account info, and chat messages. The damage can be serious, especially for young users who may not know how to protect themselves online.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
