Key points
- Malware has reached nuclear facilities: Slammer disabled monitoring computers at Davis-Besse (US) in 2003, and NPCIL confirmed malware on Kudankulam’s administrative network in 2019.
- Stuxnet damaged centrifuges at Iran’s Natanz enrichment facility despite its isolation from the internet.
- No incident has affected reactor safety systems, which are designed to work without networked computers; the main risks are loss of monitoring, data theft and forced shutdowns.
What this article covers: what Stuxnet, the Davis-Besse worm and the Kudankulam malware show about cyber risk at nuclear facilities, and how plants defend against it.
Its place in the series: the series’ look at the highest-consequence facilities, including the most significant incident at an Indian nuclear plant.
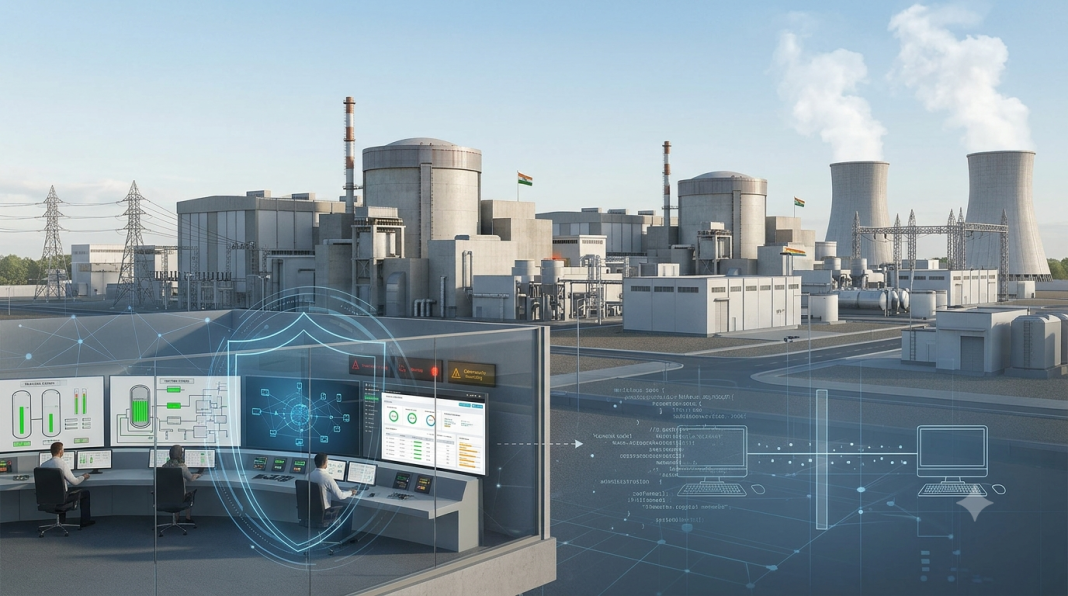
Nuclear facilities are built around layers of physical safety: containment, independent cooling and shutdown systems, and strict separation between plant controls and the outside world. Cyberattacks test whether that separation holds in practice. This article looks at three real incidents, from a worm that reached an American plant’s monitoring computers to malware found inside India’s largest nuclear power station, and at what they show about the limits of “air gaps”.
Stuxnet: the attack on Natanz
Stuxnet, discovered in 2010, targeted Iran’s uranium-enrichment facility at Natanz, not a power plant. Technical analysis by Symantec (W32.Stuxnet Dossier) and by Ralph Langner (To Kill a Centrifuge) showed that it reprogrammed Siemens controllers to make centrifuges spin outside safe limits while showing operators normal readings. Natanz was isolated from the internet, so the malware is widely understood to have arrived on infected removable media or through contractors. Stuxnet showed that an air gap reduces risk but does not eliminate it.
Davis-Besse, 2003: a worm inside a US nuclear plant
In January 2003, the Slammer worm reached the network of the Davis-Besse nuclear plant in Ohio through a T1 data connection that bypassed the plant’s firewall. It disabled the plant’s Safety Parameter Display System and plant process computer for several hours. A software patch that would have blocked the worm had been available for six months. The plant was in a safely defueled condition at the time, and the US Nuclear Regulatory Commission said the affected systems do not themselves affect the safety of the facility (NRC correspondence, 2003). The incident is a case study in how a single unmanaged connection can undermine a carefully segregated network.
Kudankulam, 2019: malware at India’s largest nuclear plant
In October 2019, the Nuclear Power Corporation of India (NPCIL) confirmed that malware had been found at the Kudankulam Nuclear Power Plant in Tamil Nadu. NPCIL said it had detected the infection on 4 September 2019 on a computer connected to the plant’s internet-facing administrative network, that this network is isolated from the critical internal network, and that plant systems were not affected (POWER magazine). Security researchers identified the malware as Dtrack, a remote-access tool associated with North Korea’s Lazarus group (Security Affairs). The incident became public only after a former government security analyst posted about it; a plant official at first dismissed the reports before NPCIL confirmed the infection.
Kudankulam is important for two reasons. It shows that state-linked groups are interested in nuclear facilities in India, and it shows that administrative networks, which hold staff credentials, documents and plant information, are themselves worth protecting even when control systems are isolated.
Why the physical safety layers matter
None of these incidents caused a radiological release, and that is not luck alone. Nuclear plants are designed so that critical safety functions, such as shutting down the reactor and cooling the core, can work without relying on networked computers. The realistic cyber risks are therefore:
- Loss of monitoring, as at Davis-Besse, which makes it harder for operators to see what is happening.
- Theft of plant information that could help plan a later attack, as feared at Kudankulam.
- Manipulation of process equipment, as Stuxnet did at an enrichment facility.
- Forced shutdowns that cut electricity supply and test the grid, linking this risk to attacks on power grids.
How nuclear facilities defend
The International Atomic Energy Agency’s guidance treats computer security as part of nuclear security, requiring national strategies, regulation and security programmes for digital systems whose compromise could affect safety or security (IAEA Nuclear Security Series No. 42-G). In practice this means:
- Grading systems by their importance to safety and isolating the most important ones completely.
- Strict control of removable media and contractor laptops, the routes Stuxnet is believed to have used.
- Prompt patching and monitoring of administrative networks, the weak points at Davis-Besse and Kudankulam.
- Transparent incident reporting, so that lessons are shared quickly.
Nuclear plants use the same kinds of controllers discussed in cyberattacks on industrial control systems and the Triton attack on safety systems. The series overview sets out how these risks connect.
Frequently asked questions
Has a nuclear power plant been hacked?
Yes, malware has reached nuclear plant networks. In 2003 the Slammer worm disabled monitoring computers at the Davis-Besse plant in Ohio, and in 2019 NPCIL confirmed malware on an administrative network at India’s Kudankulam plant. In neither case were reactor safety systems affected.
What happened at Kudankulam nuclear power plant in 2019?
NPCIL confirmed that malware, identified by researchers as Dtrack and linked to North Korea’s Lazarus group, was found on a computer on the plant’s internet-connected administrative network. NPCIL said this network is isolated from the critical internal network and plant systems were not affected.
Did Stuxnet attack a nuclear power plant?
No. Stuxnet targeted Iran’s uranium-enrichment facility at Natanz, damaging centrifuges by reprogramming the Siemens controllers that ran them.
Can a cyberattack cause a nuclear meltdown?
Nuclear plants are designed so that reactor shutdown and core cooling do not depend on networked computers, which makes a cyber-caused meltdown very unlikely. The realistic risks are loss of monitoring, theft of plant information, manipulation of process equipment and forced shutdowns.
How are nuclear plants protected from cyberattacks?
IAEA guidance calls for national computer security strategies and programmes. Plants isolate safety-critical systems, control removable media and contractor devices, patch and monitor administrative networks, and report incidents.
Last reviewed: 22 October 2026.