

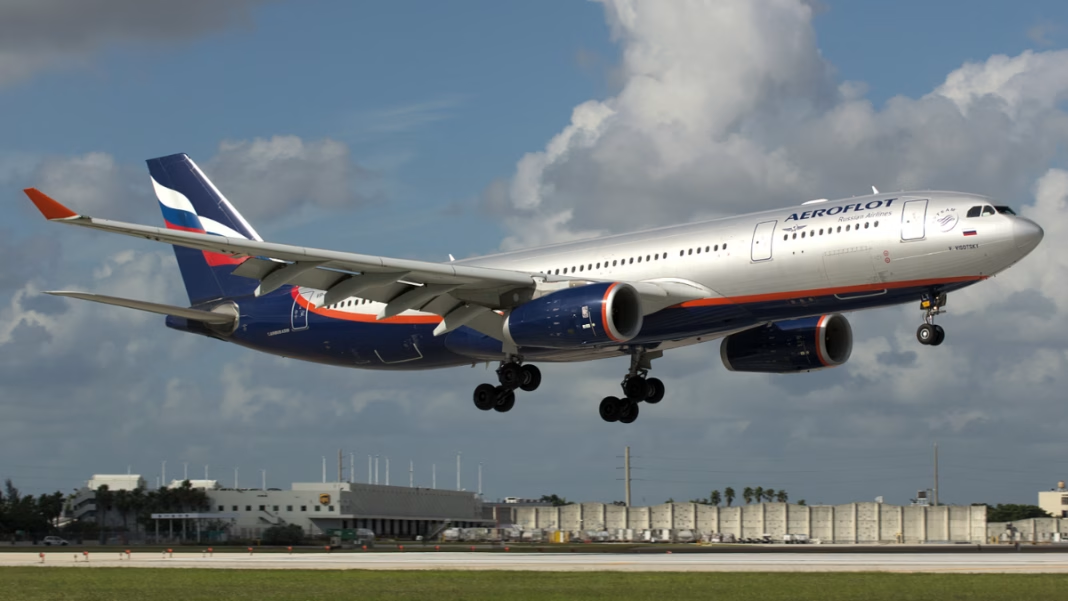
Belarusian hackers destroy Aeroflot servers, steal 22 terabytes of data in targeted cyber operation

Belarusian hackers take credit for Aeroflot cyberattack

A group of Belarusian hackers has claimed responsibility for a powerful cyberattack on Aeroflot, Russia’s largest airline. The group, known as Silent Crow, said the operation was not only meant to cause damage but also to send a clear warning to Russian authorities.

In a statement posted on the encrypted messaging app Telegram, Silent Crow revealed that it had secretly gained access to Aeroflot’s systems and stayed inside for nearly a year. During this time, the group says it mapped out the airline’s entire IT network and carefully prepared for the attack.

“We didn’t just hack them. We lived inside their system,” the hackers wrote. According to their message, the attack was carefully planned to show how weak and outdated Russia’s digital security really is.

Silent Crow was joined in the operation by Cyber Partisans, another hacker group made up of Belarusians living in exile. Both groups oppose the governments in Belarus and Russia and have been carrying out digital attacks as part of their resistance.

Hackers claim access to top-level systems and private data

The hackers said they accessed Tier0 infrastructure, the most critical level of an organization’s digital system. Tier0 access means control over core functions, such as user identities, security permissions, and key internal servers. If true, this would give the attackers nearly complete control over Aeroflot’s digital operations.

They also claimed to have taken over employee computers, including those used by the airline’s top leadership. According to Silent Crow, they viewed private company files, monitored internal communication channels, and even accessed wiretapping servers.

Belarusian hackers destroy Aeroflot servers, steal 22 terabytes of data in targeted cyber operation

The hackers said they destroyed around 7,000 servers, both physical and virtual. They also claim to have stolen 22 terabytes of data. This includes databases, emails, internal chats, and other company documents.

The group estimates the total damage could cost Aeroflot tens of millions of U.S. dollars. More importantly, they said the attack was a way to expose the failure of Russian cybersecurity systems.

“This was a message to Russia’s security agencies. Your systems are not safe,” they said.

Attack caused major flight delays across Russian airports

The cyberattack had real-world consequences. On July 28, Aeroflot announced that its information systems had been disrupted. This led to a wave of flight cancellations and delays across airports in Moscow and St. Petersburg.

From Moscow, 19 flights were cancelled and 16 were delayed, while 16 more were cancelled on the return leg. In St. Petersburg, 6 Aeroflot flights were cancelled and 9 delayed, along with more delays on flights heading back.

Aeroflot blamed the problems on a “forced adjustment to the flight schedule,” but gave few details. As travelers waited in terminals, Silent Crow released its public statement taking credit for the attack.

The hacker groups said this operation was also aimed at Russia’s cybersecurity agencies, including the Federal Security Service (FSB) and the National Coordination Center for Computer Incidents (NCCCI).

They ended their message by saying they plan to leak parts of the stolen data in the future. “We didn’t just destroy the infrastructure. We left a trace,” the message read.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
