Shocking Malware Campaign Hijacks Email Lists to Spread Fake Crypto Wallets

Malware Campaign Targets Trusted Email Platforms

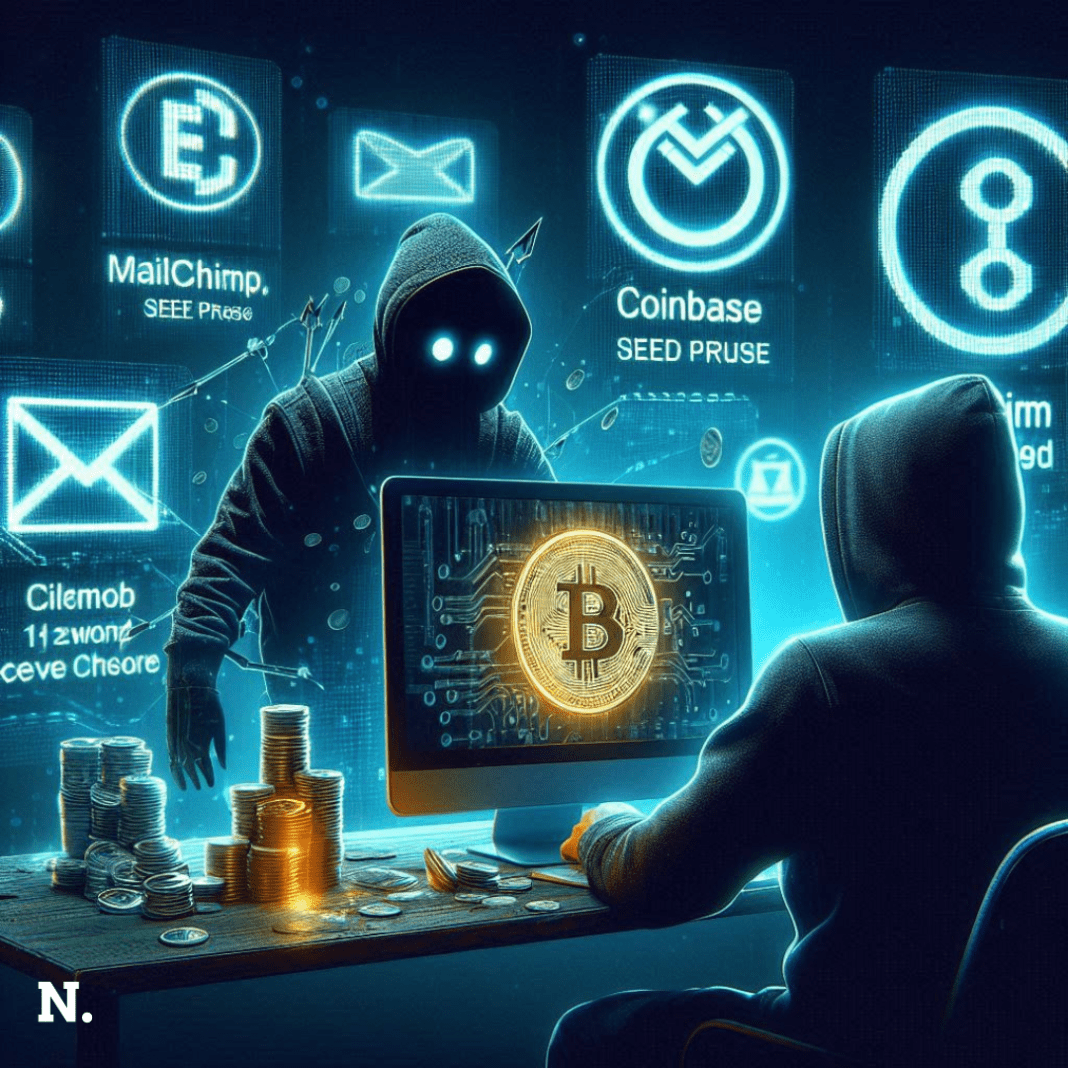
A new and dangerous malware campaign, known as PoisonSeed, has been discovered by cybersecurity experts. This sneaky scam is tricking people into handing over their crypto wallet information by using hacked email mailing lists. It’s a clever and alarming technique because it preys on the trust people have in emails from well-known platforms.

Here’s how the attack begins. The hackers first break into accounts of people who use popular email services like Mailchimp and SendGrid. These are platforms many businesses and content creators use to send newsletters to their subscribers. Once inside, the hackers quickly download all the mailing lists associated with these accounts. This means they now have access to thousands, or even millions, of email addresses—belonging to people who have signed up for trusted newsletters.

To get into these accounts, the hackers create fake login pages that look exactly like the real Mailchimp or SendGrid websites. These fake websites are so well made, it’s hard to tell the difference. Victims receive an urgent email saying there’s a problem with their account. Scared they might lose access to their tools, some users enter their passwords on the fake site—giving the hackers full control.

Fake Crypto Emails Trick Subscribers

Once the hackers have the mailing lists, they move to the next phase of the attack. They send emails to all the subscribers on these lists. The emails pretend to be from trusted crypto companies, like Coinbase. They say that the company is moving to a new kind of wallet—a self-custodial wallet.

The email then provides a 12-word seed phrase and tells the recipient to enter it into their crypto account. A seed phrase is like a secret key that gives full access to a crypto wallet. But here’s the trick: anyone who enters that phrase into a real wallet is not getting a new wallet—they’re giving hackers full access to their existing one.

In simple words, it’s like someone gives you a new key and tells you to use it in your front door. But that key was made by a thief, and the moment you use it, you’ve actually handed over the keys to your house.

People who believe the email and enter the fake seed phrase can have their entire crypto balance stolen in seconds. And because these emails come from real, trusted newsletters they’ve subscribed to in the past, many don’t even think twice before clicking.

Critical Vulnerabilities: The Dark Side of Pacemaker Technology

Smart and Subtle Phishing Tactics

What makes PoisonSeed especially dangerous is how clever it is. These emails don’t shout or scream warnings. They don’t use scary words like “Account Suspended” or “You’re in Danger.” Instead, they use a soft touch. They create just enough worry to make people act quickly, without thinking deeply.

The fake login pages used by the attackers are almost impossible to tell apart from the real ones. They use the same design, logos, and even links. This makes it much easier for victims to fall for the scam.

The campaign appears to be very organized and fast. As soon as a hacker gains access to a mailing list, they start sending out the fake Coinbase messages in bulk. Everything is likely automated, which means thousands of phishing emails can be sent out in minutes.

This campaign shows how online threats are evolving. It’s not just regular users who need to be careful—creators and businesses with mailing lists also need to stay alert. When their accounts are hacked, it’s their followers who pay the price.

How Cyber Attacks on Industrial Control Systems Can Endanger Lives ?
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories