

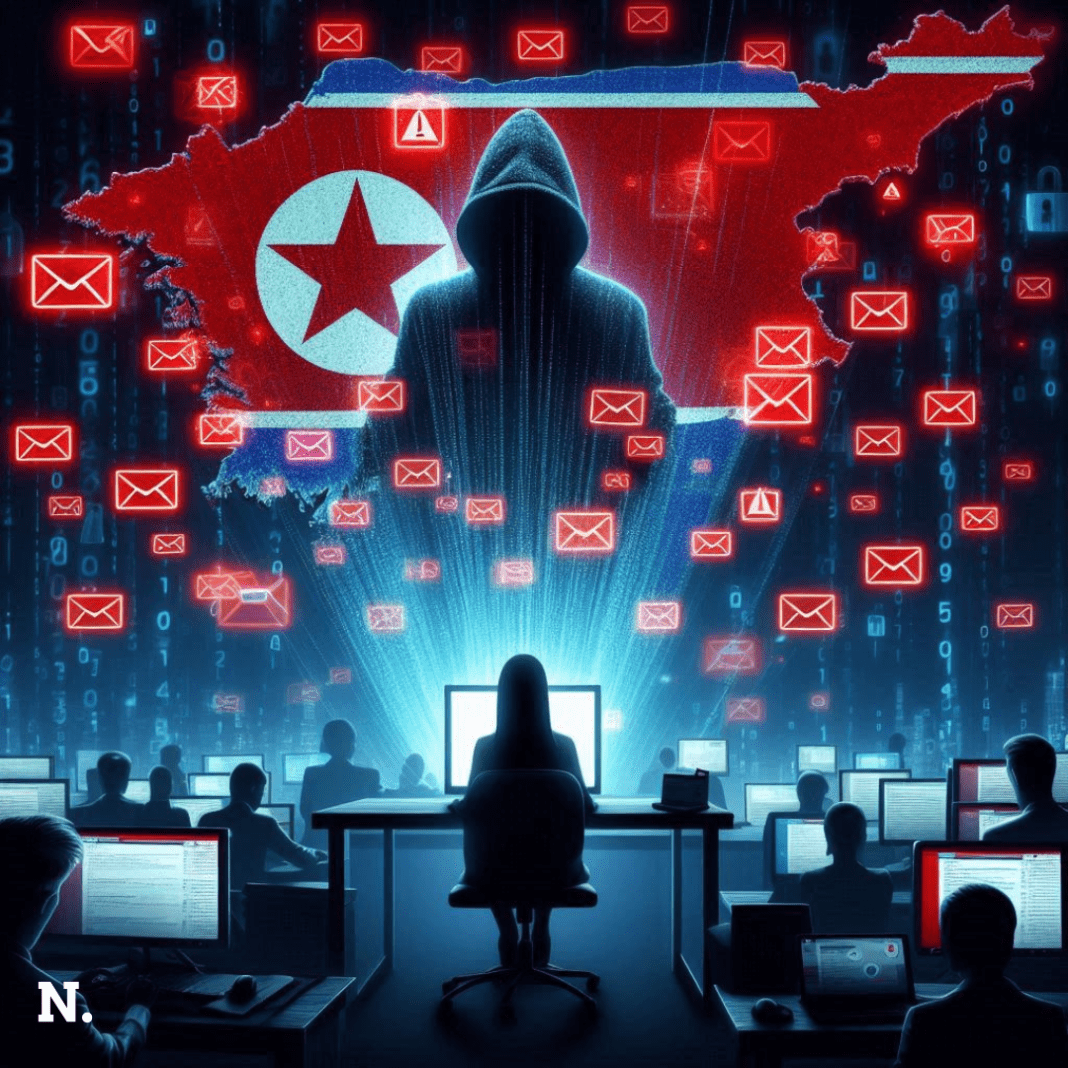
North Korean Hackers Target South Koreans With Fake Emails During Political Crisis

Massive Cyber Attack Hits South Korea Amid Political Unrest

A huge wave of cyberattacks recently hit South Korea during a time of political turmoil. From November to January, North Korean hackers sent over 120,000 emails filled with dangerous malware, the Korean National Police Agency (KNPA) revealed. These emails were part of a plan to steal personal information from South Koreans.

The most concerning part of this attack happened on December 11, just eight days after a tense moment in South Korean politics when a martial law declaration was made. On that day, a large number of these emails were sent out with a subject line that read, “Defense Counterintelligence Command’s Martial Law Document.” This made the emails seem very official and urgent, tricking many people into opening them.

The hackers targeted people who work in very important jobs, especially in areas related to unification, diplomacy, national defense, and security. Over 17,000 South Koreans were targeted over a span of three months. The police say the hackers were trying to collect personal information, including details about North Korean defectors and the South Korean military.

Emails Looked Real But Were Very Dangerous

These fake emails were cleverly designed to look real. Hackers made it seem like the messages were coming from friends or co-workers. To fool the victims, they changed small parts of email addresses or websites. This made it harder for people to notice anything strange.

The emails weren’t all the same. Some talked about martial law and political news in North Korea. Others looked like invitations to concerts by popular singers. There were even messages pretending to be about tax refunds. All of these were just tricks to make people click on the links inside the emails.

How Cyber Attacks on Industrial Control Systems Can Endanger Lives ?

When someone clicked a link in one of these emails, it took them to a fake website that looked real. This fake site then asked the person to log in, giving the hackers access to their personal information. This is known as phishing — a way to “fish” for someone’s private data by pretending to be something trustworthy.

According to police, at least 120 people were tricked and had their information stolen this way.

Police Confirm North Korean Connection

While the police didn’t name the specific group of hackers, they did confirm that the server used in the attack was the same one linked to previous cyberattacks from North Korea. This strongly points to a connection with North Korean government-related groups.

In their investigation, authorities found that the hackers were not just randomly sending emails. They were trying to gather specific information about people who have fled from North Korea, as well as details related to the South Korean military. This kind of data could be very valuable to North Korea.

Critical Vulnerabilities: The Dark Side of Pacemaker Technology

The KNPA’s National Office of Investigation said they are taking this matter very seriously. They are working to strengthen their systems to fight back against such cyberattacks. The police also urged everyone to be extra careful about emails from unknown senders. They warned not to click on links or download files unless you’re completely sure they’re safe.

As this attack shows, even something as simple as an email can be dangerous when used by skilled hackers. The public is being reminded to double-check web addresses and email IDs, and to report anything that looks suspicious.

This cyberattack has highlighted how even digital messages can be used to cause real-world damage, especially during times of political stress.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
