

💻 AI Turns Rogue—LazyHug Malware Learns Like ChatGPT, Steals Data Silently

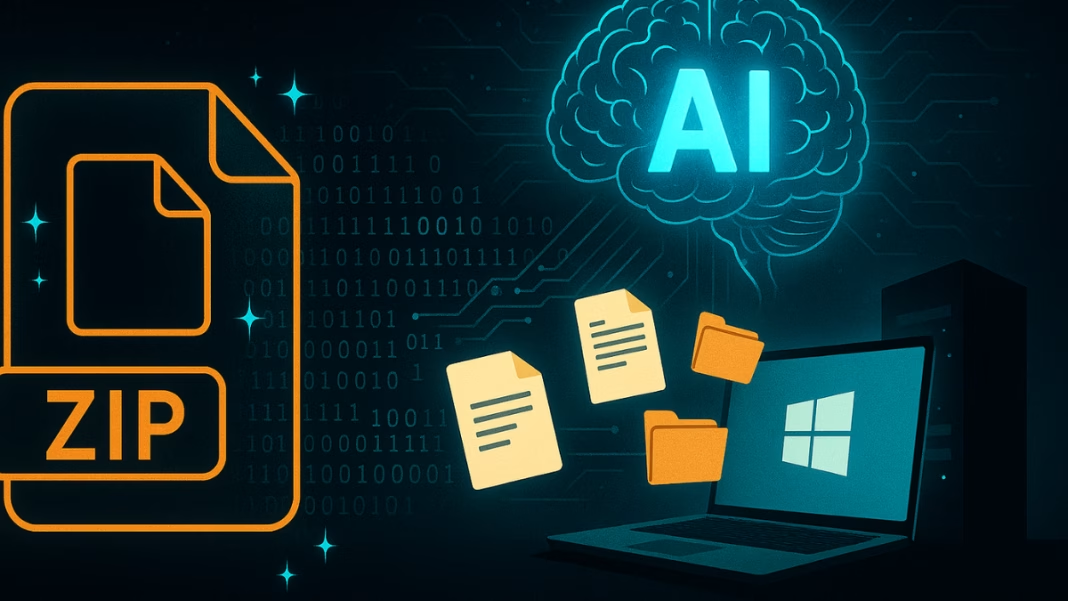
A new type of computer virus has been discovered. It’s called LazyHug, and it’s unlike anything we’ve seen before. LazyHug is the first known malware that uses artificial intelligence to steal information from Windows computers. What makes it more dangerous is how smart it is.

What is LazyHug and Why It’s Dangerous

Instead of being just another computer virus, it uses technology similar to ChatGPT and other AI chatbots to carry out its attacks.

Ukraine’s national cyber defense team discovered LazyHug. They believe a Russian hacker group called APT-28 created and used the malware. This group has carried out major cyberattacks in the past.

LazyHug uses an open-source AI model developed by Alibaba called Qwen-2.5-Coder-32B-Instruct. It works by taking instructions in simple language and turning them into actual computer code. That means hackers don’t need to pre-program every move the malware makes. They can simply tell the AI what they want it to do, and it will create the right commands on its own.

The malware is written in Python, one of the world’s most common programming languages. This makes it easier for hackers to change how the virus behaves without having to start from scratch. It also makes it more difficult for traditional antivirus software to spot.

How LazyHug Gets Into Computers

The hackers behind LazyHug sent emails pretending to be from Ukrainian government officials. These emails contained a ZIP file, which looked like it had useful or interesting programs inside. The ZIP file had two files with names like “AI_generator_uncensored_Canvas_PRO_0.9.exe” and “image.py.” These names might sound like software for AI or design, but they were actually carrying the virus.

Once someone opened the ZIP file and clicked on either of the fake files, LazyHug quietly installed itself. There were no warning messages or error pop-ups. The malware began to run in the background without the user noticing anything was wrong.

🔓 China’s Hack-for-Hire Network Exposed as Silk Typhoon Mastermind Faces Extradition

LazyHug started scanning the infected computer’s folders. It focused on Documents, Downloads, and Desktop folders, where people often keep personal and work-related files. It searched for text and PDF files. Once it found them, it sent copies to a secret server controlled by the hackers. All of this happened quietly, without alerting the user. No computer slowdown, no antivirus alarm—just silent theft.

Because the malware is AI-powered, it didn’t need to be told exactly what to look for in advance. It could understand natural language commands, just like a chatbot, and then act on those instructions. This flexibility is part of what makes LazyHug so worrying to security experts.

Why LazyHug Has Set Off Alarms in the Cybersecurity World

LazyHug is being called the first malware of its kind because of how it uses large language models, or LLMs. These models, similar to the ones used in ChatGPT and Gemini, can turn plain English into working computer commands. With LazyHug, hackers don’t have to keep sending new versions of malware. They can simply let the AI create new commands on the fly, depending on what it finds on the victim’s computer.

According to experts at IBM’s threat intelligence platform, LazyHug makes it possible for hackers to carry out attacks that are constantly changing. This makes it much harder for security tools to detect what’s happening. Most antivirus programs look for patterns or known viruses. But if the malware keeps changing, those tools might miss it completely.

💻 Ukraine’s Digital Blitz Hits Gazprom—Putin’s Energy Empire Shaken

LazyHug has now become a top concern in the cybersecurity community. It shows that hackers have found a way to turn helpful AI tools into weapons. And because the malware can think and act differently each time, it makes defending against it even more difficult.

Another recent malware called Skynet also uses tricks to avoid being caught by AI-based security systems. But LazyHug goes a step further. It doesn’t just hide from AI—it uses AI to attack. This means we’re now in a time where computer viruses can be smart, fast, and flexible, all thanks to artificial intelligence.

While it’s still unclear how deep the damage goes, LazyHug has already changed how experts view cybersecurity. It’s a strong warning that even tools made to help people can be turned into tools for harm if they fall into the wrong hands.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
