

Cyber Attack on National Tanker Company Disrupts Iranian Merchant Ship Communications

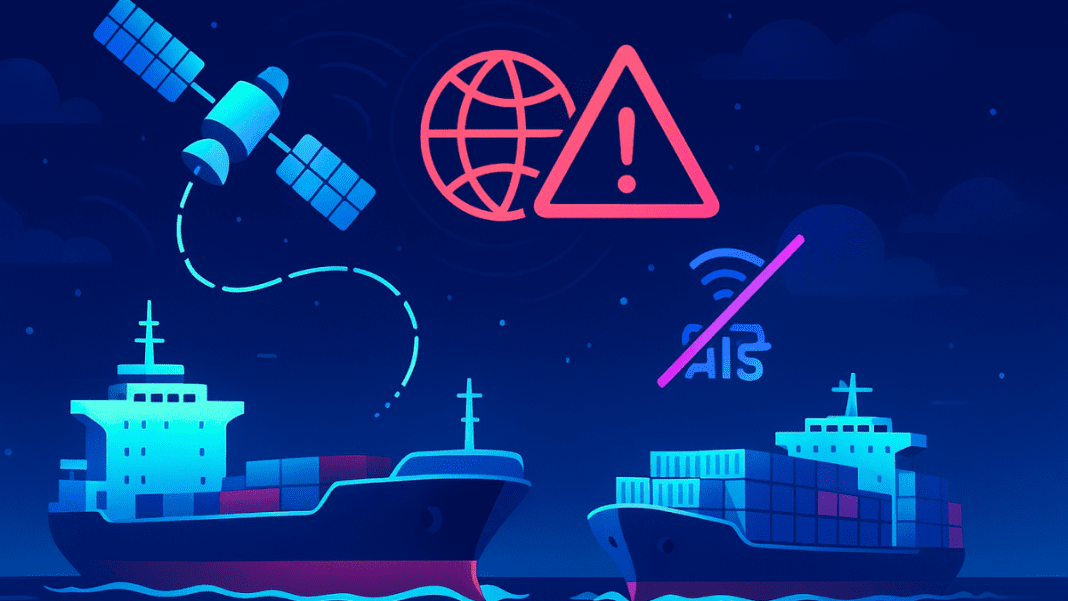
A major cyberattack has disrupted the communications of dozens of Iranian merchant vessels. A hacker group calling itself Lab-Dookhtegan has claimed responsibility for the operation.

Hackers hit Iran’s shipping networks

Reports say the attack disabled ship-to-shore communication systems of 39 oil tankers and 25 cargo ships operated by the National Iranian Tanker Company (NITC) and the Islamic Republic of Iran Shipping Lines (IRISL).

So far, NITC and IRISL have not confirmed problems. Cyber experts studied the claims and found them credible. They believe the hackers targeted ship communication networks.
This caused a large disruption in the systems.

Lab-Dookhtegan has launched similar attacks before. In March, it claimed to disable communications on over 100 ships. These ships were linked to the same two Iranian companies. That attack happened during military operations in Yemen. Observers see the group as part of a wider campaign. The campaign seems to target Iranian shipping activities.

How the hackers broke into systems

The hackers targeted Fanava Group, a private IT firm in Tehran. Fanava provides internet and satellite services for ships. It also runs networks used by merchant vessels.
The company operates a cybersecurity system called Falcon. Hackers claim they broke into this system.

The hackers broke into these systems. They blocked ship-to-shore communications.
They also disrupted AIS tracking. AIS helps ships share their location and movements.
Ports and coastal authorities use this information. Without AIS, it is harder to track ships.
This creates serious risks for safe navigation.

How Cyber Attacks on Industrial Control Systems Can Endanger Lives ?

Although little is known about Lab-Dookhtegan itself, the group seems to focus on Iranian targets. Cybersecurity experts have examined the techniques used in this latest attack and judged them as credible. An Israeli maritime cybersecurity company has stated that the tactics matched known cyber warfare methods.

Fanava, the company targeted in the attack, runs satellite networks and even financial services in Iran. Despite its central role in these sectors, the company does not currently appear on sanctions lists maintained by the US, UK, or EU. This makes the targeting of its systems particularly sensitive, as it highlights how companies not directly under sanctions can still be drawn into the conflict surrounding Iranian oil and shipping.

Growing pressure on Iran’s shipping activities

Iran’s shipping sector has long been under scrutiny because of international sanctions related to oil exports. In recent months, both the United States and the United Kingdom have expanded their enforcement to include not just ships, but also service providers linked to Iranian oil trade.

While US authorities have been aggressive in issuing fines and penalties for sanctions breaches, the UK has faced criticism for weak enforcement. Reports note that US regulators imposed hundreds of millions of dollars in fines this year alone, while UK authorities have taken only a few actions, none of them linked to Iranian oil.

Insider revenge cyberattack freezes 1,000 workers — Eaton hit with massive disruption and losses

Enforcement is a major challenge because of the complex networks Iran’s shipping activities rely on. These networks often use front companies, hidden ownership, and offshore service providers to avoid detection.

The latest hacking incident shows how Iran’s shipping operations remain exposed to both sanctions enforcement and cyber operations.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
