

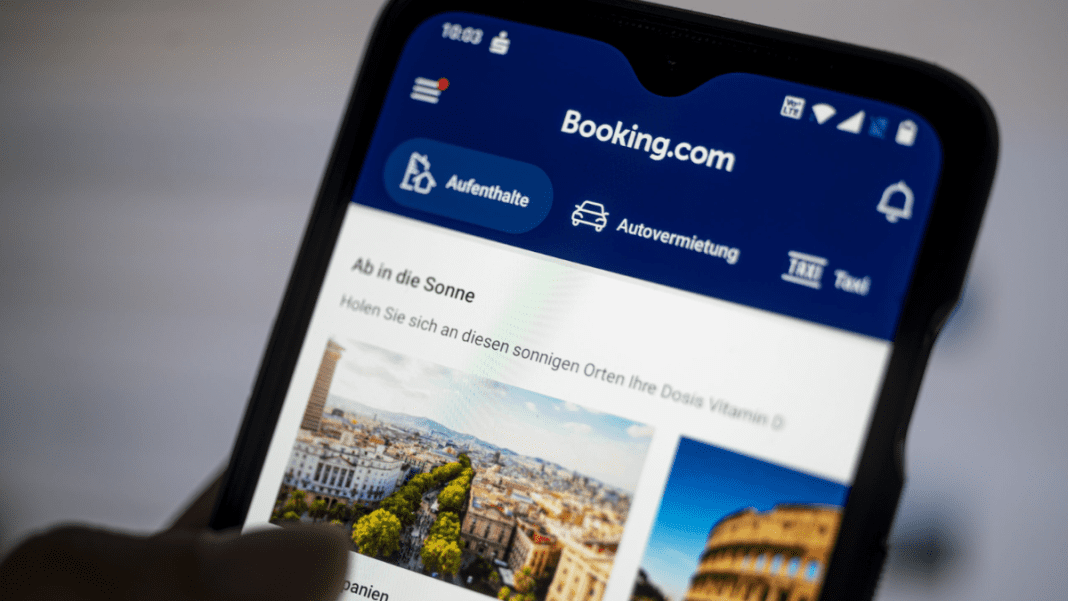
Australians warned as fake Booking.com sites spread dangerous XWorm malware

Australians are facing a rise in online scams. These scams look like trusted travel websites. Fake Booking.com pages are tricking people. Victims click, download, and install dangerous malware without knowing it. Cyber experts are warning about this threat. The warning comes during Scam Awareness Week. Criminals are becoming smarter. They now target both everyday travellers and large organisations.

Fake Travel Websites Designed to Trick People

New research has found a campaign of fake websites. These sites copy the travel platform Booking.com. At first glance, they look almost the same as the real website. But the fake site blurs the main page. It then shows visitors a cookie banner. The banner asks them to click “Accept” to view the page.

One click is enough for hidden malware to enter the device. After installation, the malware hides inside normal computer processes. This makes it hard to detect or remove. The virus, called “XWorm,” gives scammers full control of the device. They can open files also can switch on webcams and microphones. They can even bypass security tools.

The tactic works because of what experts call click fatigue. Many people are used to seeing cookie banners and often click quickly without thinking. By copying the look and feel of a trusted travel site, the fake pages make people believe they are visiting a legitimate website.

Reports suggest that scammers are targeting Australians more during peak travel seasons. This is the time when people are in a hurry to grab holiday deals and are less careful about the websites they visit. Researchers found at least three fake domains in February 2025, and more have appeared since, showing that the campaign is ongoing.

How Scammers Target Travellers and Businesses

While fake Booking.com sites are tricking holidaymakers, experts have also warned that supply chains are being targeted. Scams are no longer only about stealing personal information from individuals. Criminals are now building fake supplier websites, creating false compliance records, and even hiding the real ownership of companies. These tactics make it difficult for businesses to identify fraud through traditional checks.

Cyberattack Catastrophe: How Hackers Can Endanger Human Lives ?

In some cases, criminals add fake suppliers to procurement systems, causing organizations to pay large sums of money without realizing it. Businesses relying on old methods of due diligence are finding it harder to detect these scams.

Modern fraud attacks are harder to spot. They are designed to blend in. Criminals add small details that look real. They build many layers of lies. Some use fake certificates. Others use false papers or copy websites. These tricks can fool human reviewers. Experts say companies should use advanced tools to find these risks. Artificial Intelligence can scan large amounts of data and spot hidden signs.

Rising Need for Proactive Security

Across Australia, there is a clear warning that scams are no longer simple or obvious. Cybercriminals are adapting their tricks faster than ever, and the use of fake travel websites is only one example of how scams are evolving to fit current events and consumer behavior.

Security teams are being advised to move away from reactive methods and adopt proactive approaches. This means collecting and analyzing information about new scams as they emerge, instead of waiting until after an attack has already happened. By spotting trends and patterns early, organizations can identify weaknesses before scammers exploit them.

How India’s Facial Recognition Tech Could Be a Disaster for Privacy

Security researchers have emphasized that while automated systems and Artificial Intelligence are powerful, they cannot fully replace human judgment.

As cybercriminals continue to copy trusted brands like Booking.com, both individuals and businesses are urged to stay alert. For travellers, this means using official apps, entering website addresses manually, or booking through reputable agencies instead of relying on random links.

Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
