
The Federal Bureau of Investigation (FBI), the main law enforcement agency in the United States, has issued an official warning about a sharp increase in ATM jackpotting incidents during 2025. Authorities reported hundreds of cases across the country, drawing attention to a growing form of cybercrime that directly targets cash machines rather than customer bank accounts.
Data shared by investigators shows that Automated teller machine jackpotting is becoming more frequent and more organized. The activity involves criminals using both technical knowledge and physical access to machines. The rise in reported cases has highlighted the financial risks facing banks, ATM operators, and the broader payment system.
Surge in ATM Jackpotting Cases Reported by the FBI
According to the FBI, more than 700 ATM jackpotting incidents were recorded across the United States in 2025. This number reflects a clear increase compared with previous years and suggests coordinated activity by organized criminal groups.
FBI Informant alleges Epstein relied on a personal hacker for gaining sensitive digital access
Financial estimates show that these attacks have caused major losses. Since 2020, criminals have extracted more than $20 million through jackpotting operations. Investigators noted that over $12 million of these losses occurred in 2025 alone, showing how quickly the threat has intensified.
Unlike traditional fraud that targets cardholders, ATM jackpotting focuses on the machine itself. Criminals bypass normal transaction controls and force the ATM to release cash directly. Because the attack happens at the machine level, banks may not immediately detect the unauthorized withdrawals.
Authorities say the pattern of incidents indicates careful planning. Many attacks follow similar methods, suggesting shared tools and knowledge among criminal networks. The FBI warning highlights the growing scale of this activity and its impact on financial infrastructure.
How Criminals Carry Out ATM Jackpotting Attacks
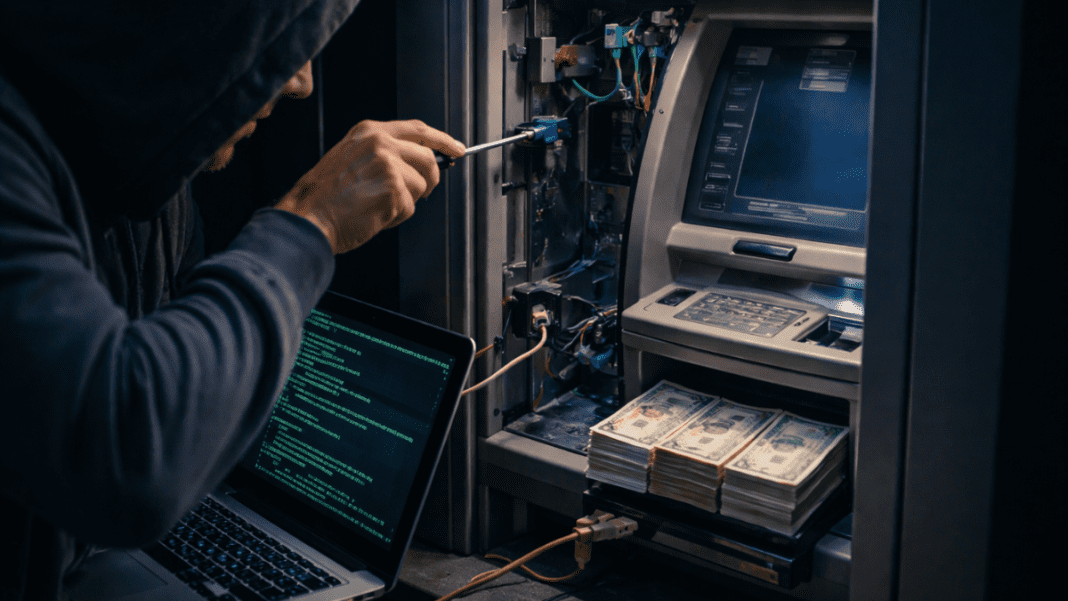
ATM jackpotting combines physical intrusion with cyber techniques. Attackers usually begin by opening the ATM cabinet to access internal hardware. This allows them to interact with the computer system that controls the machine’s operations.
Once inside, criminals may install malicious software onto the ATM’s hard drive or replace the drive with one that contains preloaded jackpotting malware. After activation, the software gives attackers control over the cash dispensing mechanism.
Using external devices such as mobile phones, keyboards, or specialized tools, criminals can trigger the ATM to release large amounts of money without a legitimate transaction. The process can be completed quickly, allowing attackers to collect cash before detection.
In more advanced situations, the malicious software can spread across connected ATM networks. If machines share communication systems, multiple ATMs may be affected at the same time. This increases the total financial damage and complicates response efforts.
Security analysts note that these attacks often exploit weak physical locks, outdated operating systems, or limited monitoring. When these vulnerabilities exist together, they create opportunities for jackpotting operations to succeed.
Role of Ploutus Malware and Growing Cybercrime Activity
One of the tools frequently linked to ATM jackpotting is Ploutus malware. This software is specifically designed to target ATM environments and control the cash dispensing function. Ploutus allows attackers to send commands that instruct machines to release money on demand.
The malware can be triggered by FBI through direct connection to the Automated teller machine or through coded instructions delivered via external devices. Its design makes it suitable for coordinated operations involving multiple attackers working at different locations.
The FBI alert emphasizes that the use of tools like Ploutus demonstrates increasing technical sophistication among cybercriminal groups. These operations show a shift from simple scams toward attacks on financial infrastructure itself.
From 57,000 to 5,500: FBI Sharply Cuts Back Surveillance of Americans Under
Section 702
Authorities also highlight the importance of physical access in many jackpotting incidents. Machines located in isolated or less monitored areas may face higher risk because attackers need time to open cabinets and install malware. At the same time, delays in software updates or security patches can make machines easier to compromise.
The reported surge in ATM jackpotting cases during 2025 reflects a combination of organized planning, specialized malware, and vulnerabilities in both hardware and software systems. The FBI warning brings attention to how these factors are contributing to a growing category of financial cybercrime affecting ATM networks across the United States.