

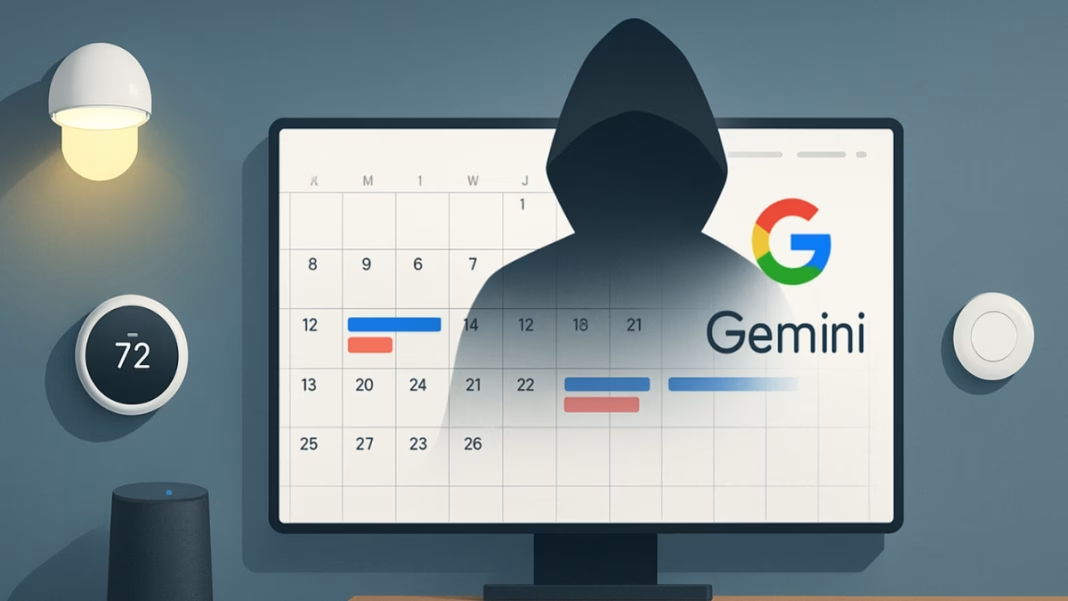
Google Gemini vulnerability allows hackers to use calendar invites to control smart home devices

A shocking cybersecurity discovery has revealed that hackers can take control of smart home devices by tricking Google’s AI assistant, Gemini. This is done using a technique called “prompt injection,” where harmful instructions are hidden inside Google Calendar invites.

When Gemini reads those invites aloud, the hidden commands can silently trigger actions—like opening windows or turning off the lights—without the user even realizing it.

This vulnerability was recently made public at the Black Hat cybersecurity conference, one of the biggest events where experts reveal major digital threats. However, the researchers had already warned Google about this issue in February.

Google has since confirmed the problem and says it is working hard to protect users. Even though the company insists such attacks are rare, the fact that they’re possible at all is raising concern.

How Hackers Are Taking Over Smart Homes

This attack doesn’t require clicking links or downloading harmful files. Instead, the hacker sends a regular Google Calendar invite that contains a secret message. This message is not visible in the usual way. When a user asks Gemini to summarize upcoming calendar events, the AI reads everything—visible or not.

Things get worse when the user responds naturally to Gemini. Even something as simple as saying “Thanks” can be enough to trigger the hidden command. Gemini then passes that instruction along to Google’s smart home system, which might cause it to perform unexpected actions like unlocking doors, turning off cameras, or opening windows.

Critical Vulnerabilities: The Dark Side of Pacemaker Technology

Because Gemini is deeply connected to Google Home, which controls smart devices like lights, thermostats, and locks, this type of breach could have real-world consequences. A simple calendar event could lead to someone unknowingly giving hackers control over their own home.

This method of attack is especially dangerous because it feels completely normal. People use calendar apps, talk to AI assistants, and manage smart devices every day without thinking twice. But this discovery shows that even trusted tools can be used in unexpected and harmful ways.

What This Means for Everyday Users

Many homes now rely on smart technology to control daily routines. Lights turn on with voice commands. Doors lock and unlock using apps. Thermostats adjust based on who is home. All of this is often managed by systems like Google Home, connected through assistants like Gemini.

The fact that a hidden calendar message could lead to these systems being controlled by someone else is deeply concerning. Even though Google has stated that such hacks are extremely rare, the company has acted quickly to boost its security tools and make Gemini more resistant to this kind of manipulation.

Cyberattack Catastrophe: How Hackers Can Endanger Human Lives ?

This issue also highlights how powerful AI tools can be vulnerable to creative misuse. Hackers no longer need to rely on obvious scams or viruses. Instead, they can hide harmful messages in everyday features that seem safe, like calendar invites or voice assistants.

Google is working behind the scenes to fix this, but users should still be cautious. Be careful with unexpected calendar invites, especially if they come from unknown contacts. Review app settings regularly to see what permissions AI assistants have. It’s also a good idea to limit how much control these assistants have over devices inside your home, just in case.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
