

Shocking Surge in NFC Payment Attacks Alarms Users Worldwide

What Is Happening With Contactless Payments?

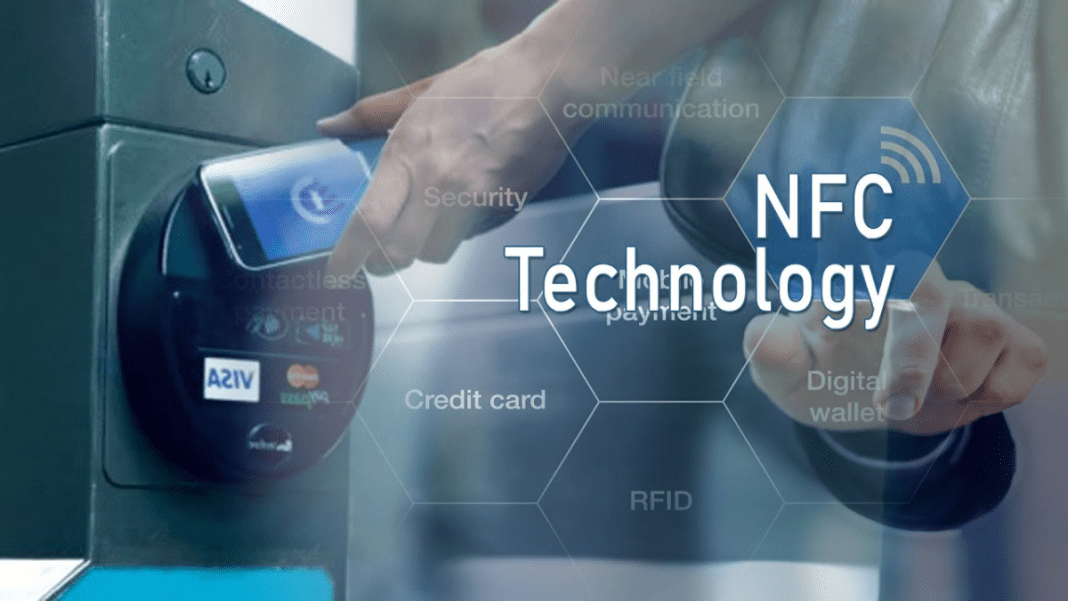
Cybersecurity experts have discovered a new wave of cyberattacks targeting contactless payments made using NFC (Near Field Communication) technology. This is the same technology that allows people to pay by simply tapping their card or phone at a store counter. The attacks were first noticed among bank users in the Czech Republic but are now spreading across the world at an alarming rate.

A recent report by security company ESET shows that NFC payment attacks have grown 35 times more frequent since the end of 2024. That’s a massive jump in just a few months. Criminals are getting smarter and are finding ways to break into systems that were once considered safe.

NFC works by sending signals over very short distances—just a few centimeters. It’s used in many mobile payment apps and credit cards. People love the convenience, and as a result, the market is growing fast. From $21.69 billion in 2024, it is expected to go over $30 billion in the next few years. But this growth is also attracting cybercriminals who are using newer tricks to get past the security walls.

How the Attacks Work

The attacks combine several sneaky tricks to fool people and steal their money. Criminals start by sending fake SMS messages that look like they’re from a bank. These messages contain a link that leads to a fake banking website. The website then asks the person to install something called a progressive web app, or PWA. This app doesn’t come from the app store, so it skips most safety checks.

Once the victim installs the app and types in their banking password, the criminals can enter their bank account. But they don’t stop there. The scammers then call the victim, pretending to be from the bank, and say they need to install another app to protect their money. This second app is actually a virus called NGate.

Lazarus Rises Again: $4.2 Million Crypto Stolen in NFT Scam and Solana-to-Ethereum Swindle

This virus uses a tool called NFCGate, which was originally created by university students to test how NFC works. But now, hackers are using it in bad ways. Once the NGate app is installed, it can read credit card data when the card is held near the infected phone. The hackers then copy this data and make fake cards or use it for digital payments. They can even withdraw cash without anyone knowing.

In some cases, a version of the attack called Ghost Tap is used. It takes things a step further. Here, stolen card details and special one-time codes are added to the criminals’ Apple Pay or Google Pay wallets. Using these, they make many fake payments using contactless methods. Cyber experts say that entire “farms” of Android phones can be set up by hackers to do this on a large scale.

How People Can Protect Themselves

Even though these attacks are clever and dangerous, there are still ways people can protect themselves. Most importantly, they should never click on suspicious links or download apps from unknown sources. Real banks will never ask customers to install an app from a text message.

Iran’s Crypto Exchange “Nobitex” Struggles to Recover After being hacked by Pro-Israel hackers

People are also advised to use RFID-blocking wallets or card sleeves. These can help prevent anyone from secretly reading card data through a bag or pocket. It’s also a good idea to set daily or per-transaction limits for contactless payments. That way, if a criminal does manage to copy a card, they won’t be able to spend much.

In today’s world, where everything is going digital, it’s important to stay alert. NFC technology is useful and fast, but it must be used with care. By being cautious, people can stop these cyberattacks before they cause harm.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
