

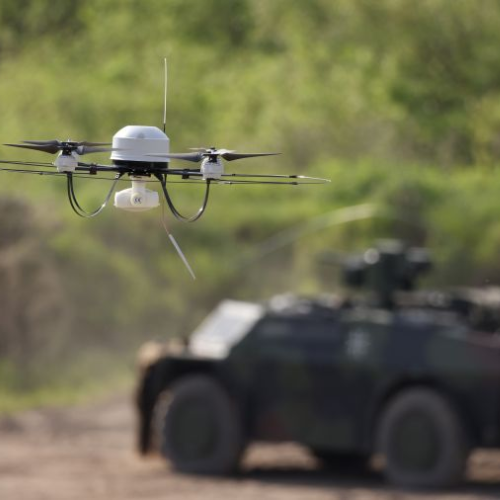
Hackers Masquerade as Drone Sellers to Launch Devastating Spy Campaign in Ukraine

Hackers are using a sneaky new trick to spy on people in Ukraine. They are pretending to be drone seller companies and official government groups to fool their victims. Once they gain trust, they send harmful files in emails. These files can secretly steal important information from computers.

Fake Emails, Real Threats

This new hacking campaign started in February and targets Ukraine’s armed forces, police departments, and local government offices—especially those close to Ukraine’s eastern border near Russia. These areas are already under a lot of pressure because of the ongoing conflict, and this cyberattack adds another serious problem.

The emails are sent from real but stolen accounts. This means that hackers get into someone’s email and use it to send fake messages. The emails look trustworthy because they come from people the victims already know or work with. That makes it more likely that the victim will open the email and click on any links or files inside.

Hackers carefully choose the subject lines of the emails to catch attention. They mention topics like clearing landmines, paying fines, building drones, or receiving money for homes destroyed in the war. All of these are real concerns for many Ukrainians, which makes the emails seem even more believable.

Sneaky Chaos: Drone Embedded Malware Shakes Up Russia-Ukraine War

Malware that Spreads through Drone Sellers

Inside these emails are files or attachments that hide two types of malware—bad software meant to cause harm or steal information.

The first type is a script, or a set of instructions, taken from a public GitHub page. GitHub is a website where computer programmers share code. While most of this code is used for good purposes, hackers sometimes find and use it for harmful reasons.

The second type of malware is more dangerous. It is called GiftedCrook. This malware is made to sneak into web browsers like Google Chrome, Microsoft Edge, and Firefox. Once inside, it steals cookies, browser history, and saved passwords.

Cookies are small pieces of data that keep you logged into websites, and saved passwords are exactly what they sound like—your login information. If someone steals these, they can easily break into your accounts without needing to guess your password.

Cyberattack Hits Ukraine’s Railway, Causing Travel Disruptions

After stealing the data, the malware compresses it into a single file and sends it over the messaging app Telegram. Using Telegram makes it harder for defenders to detect the activity because people widely use the app and don’t normally think of it as a place where hackers send stolen information.

Who’s Behind the Attacks?

Ukraine’s cyber emergency response team, called CERT-UA, is the group investigating these attacks. They are tracking the hackers under the name UAC-0226, but they have not said which country or group is behind the activity. There are no clear signs yet that link this hacker group to others known from the past.

Even though CERT-UA hasn’t shared everything, they did show examples of the fake emails used in the attacks. One email pretended to sell drones and included pictures to make it look more real. Another email looked like a schedule for clearing landmines in a Ukrainian city. These emails are designed to play on people’s fears and hopes, making them more likely to open them.

Russian Cybercriminals Wreak Havoc on Belgian Government Sites Over Ukraine Aid

In March alone, CERT-UA discovered three separate cyberattacks aimed at government agencies in Ukraine. All signs point to a carefully planned operation. The hackers clearly studied their targets and knew what kinds of messages would get their attention.

Cyberattacks like this are just one of many ways that digital warfare is being used in today’s world. While the damage may not be visible like in a traditional attack, the impact can be huge—especially when it involves military, police, and government systems.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
