

Football Comments or Spy Codes? Russian Espionage Went Undetected for 23 Years

For over 20 years, Andreas and Heidrun Anschlag lived a quiet life in Marburg, Germany, pretending to be a normal married couple. To their neighbors, they seemed like any other family. Andreas worked as an engineer for a car company, while Heidrun stayed home to care for their daughter. They carried Austrian passports and claimed to be from South America. Everything about them seemed ordinary—except for one odd habit.

The couple often made long phone calls in their garden, even in freezing weather. Neighbors found it strange but never suspected anything serious. In reality, Andreas and Heidrun were Russian spies working undercover for 23 years.

Their mission was to steal secret documents from NATO, the EU, and the United Nations, and send them to Moscow. They were well-paid for their work—earning around €90,000 (about $98,000) per year. Over the years, they passed on thousands of sensitive files, putting international security at risk.

Cyberattack Catastrophe: How Hackers Can Endanger Human Lives ?

Shocking Espionage Techniques: From Radio Signals to YouTube Comments

The Anschlags initially used old-school spy techniques. They relied on shortwave radio transmissions, dead drops (hidden objects where information was secretly exchanged), and even satellite links to communicate with their Russian handlers. However, as technology advanced, so did their methods.

In early 2011, the couple made a surprising shift to using the internet for their covert operations. Instead of risky face-to-face meetings or easily traceable radio signals, they turned to YouTube—the world’s most popular video platform.

To communicate secretly, they created a YouTube account under the name @Alpenkuh1 (which translates to “Alpine Cow 1”). Meanwhile, their Russian handlers set up a separate account called @crsitanofootballer. Both accounts appeared harmless. To anyone scrolling through YouTube, they seemed like regular sports fans.

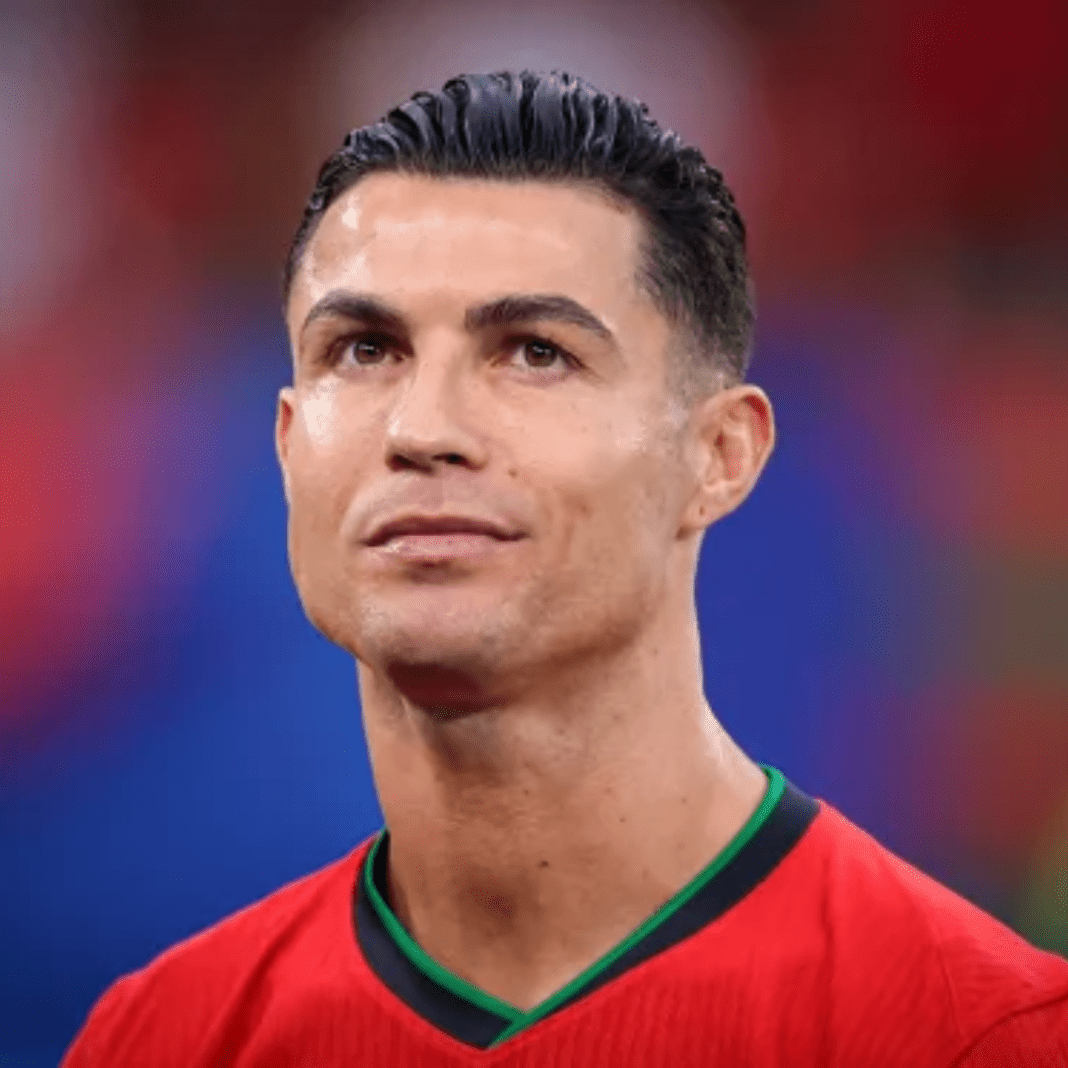
But here’s where it got clever. The spies began posting comments under videos of Portuguese football superstar Cristiano Ronaldo, who was playing for Real Madrid at the time. They would leave seemingly innocent remarks like:

  • “Great video, the song is amazing.”
  • “Ronaldo is the best!”

In response, their Russian handlers would reply with casual comments such as:

  • “He runs and plays like the devil.”
  • “That goal was pure magic.”

At first glance, these comments appeared to be typical fan chatter. However, they were actually hiding a sophisticated code. Intelligence experts later discovered that the punctuation, spacing, and arrangement of the comments followed a specific pattern. When decrypted, the messages revealed coded instructions and classified information being transmitted directly to Moscow.

This method was both brilliant and terrifying. By blending into the massive volume of YouTube traffic, the spies’ messages were nearly impossible to detect. They took advantage of the platform’s vastness and the innocent appearance of football-related content to fly under the radar.

How Cyber Attacks on Industrial Control Systems Can Endanger Lives ?

A Dramatic Arrest and the Fall of a Spy Network

Though the Anschlags seemed to live a normal life, German intelligence was already tracking them. After months of surveillance, agents raided their home in October 2011.

The arrest was dramatic. During the raid, authorities stormed into the study and caught Heidrun receiving a coded message through a radio transmitter. Shocked, she fell off her chair and unplugged the device by accident.

Even with their cover blown, the couple stayed calm. But investigators soon found plenty of evidence. They discovered encrypted USB drives, advanced radio gear, and communication logs that proved the couple was working for Russian intelligence.

Critical Vulnerabilities: The Dark Side of Pacemaker Technology

In July 2013, a German court sentenced Andreas to six and a half years in prison and Heidrun to five and a half years. Authorities also arrested a Dutch Foreign Ministry mole who had given the couple secret NATO and EU documents. He was sentenced to 12 years in prison.

But the story didn’t end there. In 2015, the Anschlags were released early and sent back to Russia in a quiet exchange deal. Despite their crimes, they were welcomed as heroes when they returned.
Cyber Attacks on Connected Cars

Mohit Kumbhar
Mohit Kumbharhttps://www.linkedin.com/in/mohitkumar99/
Mohit Kumbhar is the editor of Newsinterpretation. He edits the site’s news coverage and writes on artificial intelligence, AI search and how publishers become visible to AI assistants such as ChatGPT, Claude, Gemini and Perplexity. He also writes about NI Geovanta, the AI visibility tool for WordPress developed by Newsinterpretation.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
