

Oracle warns of extortion emails hitting E-Business Suite users amid software gaps

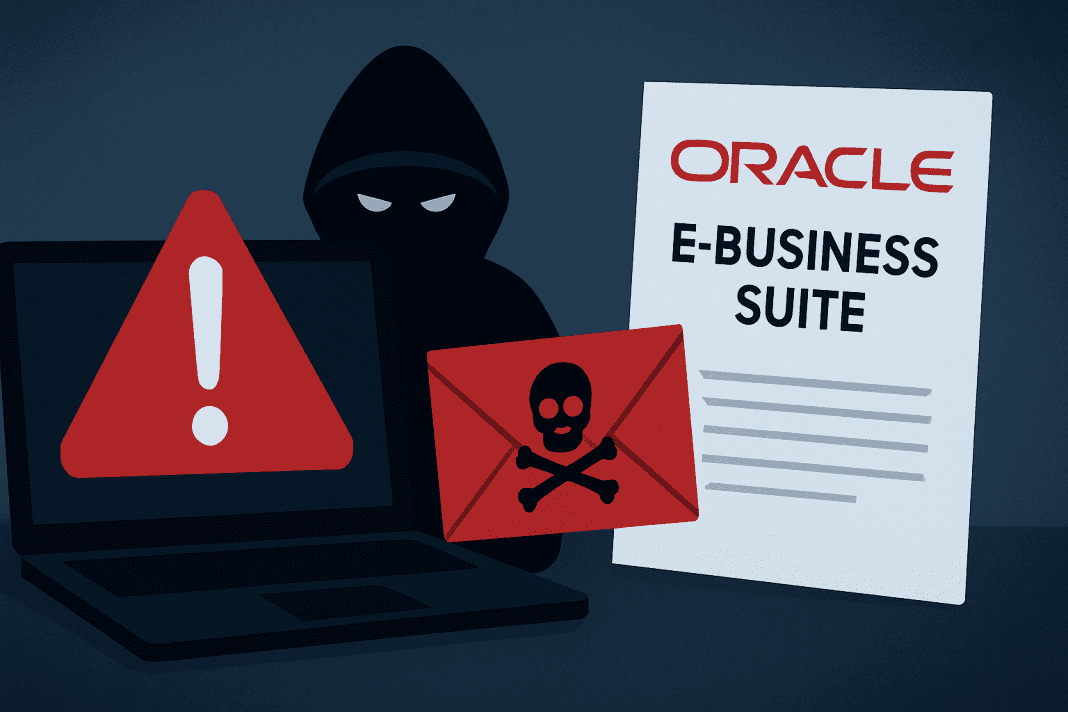
Oracle has confirmed that customers using its E-Business Suite of products have received extortion emails. The California-based tech company said that hackers may have exploited previously known software vulnerabilities. These security gaps had already been identified in past warnings, and clients were urged to upgrade their systems.

Extortion Emails Target Oracle E-Business Suite Users

Oracle emphasized the importance of updating to the latest versions of its software to prevent unauthorized access. The company has not disclosed the exact number of customers affected but confirmed the issue is serious enough to warrant attention.

Security analysts have described the attack as “high volume,” indicating that many organizations could have been targeted. The emails reportedly contained threats demanding large sums of money to avoid potential consequences, which could include data leaks or system disruptions.

AI startup Anthropic confirms cybercriminals used its Claude AI Chatbots to Launch Phishing and Ransom Attacks

The attackers appear to be focused on companies that rely heavily on Oracle’s software for business operations. Since the E-Business Suite is widely used globally, the threat could affect a broad range of industries, from finance and manufacturing to services.

Hackers Demand Massive Payments

The extortion campaign is linked to a ransomware group that operates globally. This group uses a model called ransomware-as-a-service, which means it develops malware and infrastructure and rents it to other cybercriminals. In return, it takes a cut of the ransom payments.

Security firms report that the ransom demands have ranged from millions of dollars to as high as $50 million. These figures illustrate the aggressive nature of the attacks and the high stakes for affected companies. The hackers send threatening emails to pressure organizations into paying quickly, often using fear and urgency to increase compliance.

The group behind the attacks remains anonymous, and its members’ locations are not publicly known. However, cybersecurity experts have linked the group to Russian-speaking networks. Researchers note that this group is highly adaptable, frequently changing tactics, which makes it difficult for organizations to predict or defend against their attacks.

Ukraine joins global allies to shatter elite hacker ring behind $80 million ransomware chaos

In messages reviewed by cybersecurity analysts, the group claimed that Oracle’s software “bugged up,” referring to the vulnerabilities they allegedly exploited. These warnings highlight the ongoing importance of maintaining updated software, as outdated systems can provide easy entry points for hackers.

Japanese cybersecurity firms have described this ransomware group as a “trendsetter” in its methods. Its ability to constantly evolve makes it one of the more dangerous and high-profile groups in the ransomware world. Organizations using Oracle software are being urged to stay vigilant and ensure all patches and security updates are installed promptly.

Rising Concerns in Cybersecurity

This extortion campaign adds to a growing list of high-profile cyberattacks targeting major companies and their clients. Hackers increasingly focus on widely used software, aiming to maximize impact and potential financial gain.

Oracle’s E-Business Suite is critical for many businesses in managing day-to-day operations. A successful attack could disrupt business functions, compromise sensitive data, and create financial losses. The incident underscores how vital it is for companies to maintain updated software and robust cybersecurity measures.

AI is making phishing, ransomware, and cybercrime more dangerous for accountants

Security experts note that the current campaign is a reminder of how ransomware groups continue to evolve. Their tactics are unpredictable, making cybersecurity preparedness a top priority. Companies worldwide are now paying closer attention to potential vulnerabilities and the importance of prompt software updates.

For now, Oracle is investigating the situation and advising customers to update their systems to the latest secure versions. The company has not shared detailed information about which specific clients were targeted or how the attacks were carried out. However, the warning itself highlights the ongoing threat posed by cybercriminals in today’s digital environment.
TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
