

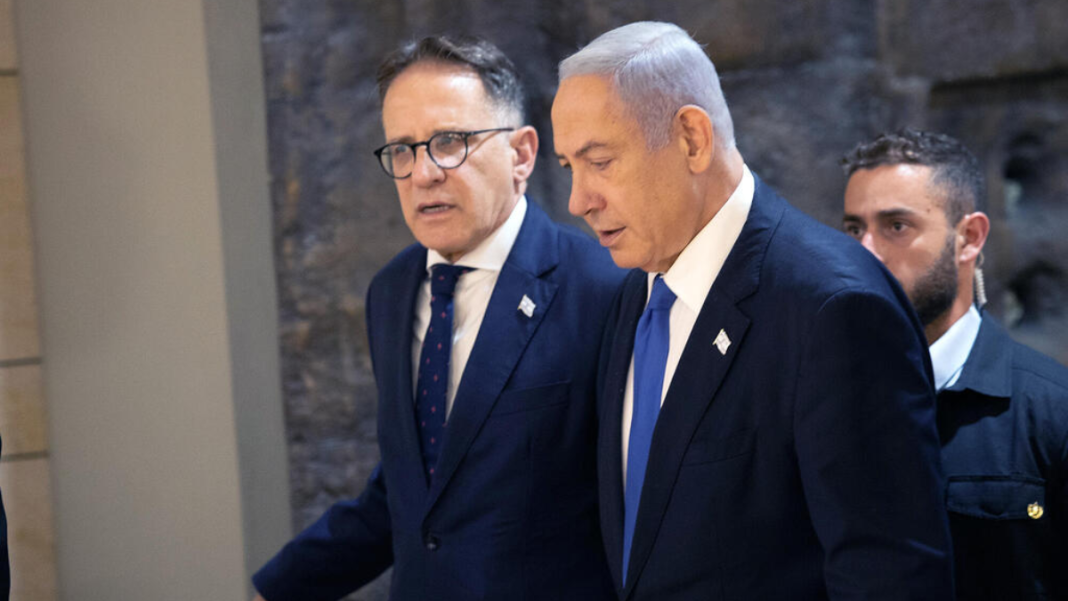
Iranian hackers breach Netanyahu aide Braverman’s phone, exposing elite Shin Bet agents guarding Israel’s top leaders

An Iranian hacking group, Handala, reportedly broke into the cell phone of Tzahi Braverman, chief of staff to Israeli Prime Minister Benjamin Netanyahu. The hackers claimed to have accessed sensitive information, including the contacts of elite security personnel responsible for protecting Israel’s top leaders.

Among the exposed contacts were 36 agents from Unit 730, a special Shin Bet security detail that guards Israel’s president, prime minister, and other high-ranking officials. In addition to these critical contacts, Braverman’s phone contained roughly 2,000 other contacts, including political figures and staff, leaving many people vulnerable to cyberattacks.

Israeli security sources described the breach as extremely serious, warning that both the agents and the individuals they protect could face grave danger. The leak coincided with Netanyahu’s visit to the United States for his fifth Oval Office meeting in a single year, raising concerns that the timing could undermine Israel’s diplomatic efforts and international credibility.

Hacker Claims and Security Implications

The Iranian hackers released statements emphasizing the breach’s impact. Handala warned that every layer of security surrounding Braverman had failed and that the contacts of top officials were now exposed. The messages were intended to demoralize Israeli leadership and sow fear, highlighting vulnerabilities in their security practices.

Iran-linked hackers targeted Israeli law firms, logistics and infrastructure in 2025 cyber surge

Although there is no proof that the hackers accessed classified intelligence beyond the contact list, the exposure of Unit 730 agents is still considered a major security failure. Revealing the names and phone numbers of elite operatives could endanger ongoing operations and compromise their safety.

Experts pointed out that the breach demonstrates how digital devices can become a major weak point in modern security. Even high-ranking officials like Braverman are vulnerable if their communications are not properly protected. This incident shows the challenges governments face in safeguarding sensitive information in the digital age.

Controversial Background of Tzahi Braverman

Braverman has been involved in several high-profile scandals in recent years. He played a role in leaking IDF intelligence documents to foreign media, including outlets in Germany and Britain. These reports were initially portrayed as secret Hamas war plans, but Israeli security authorities later determined that the documents were outdated and of little value. The incident angered the IDF, which investigated the leak, but Braverman faced no formal consequences, largely due to protection from Netanyahu.

Iran-linked hackers weaponize doxxing and bounties in escalating cyber war on Israelis

Braverman was also reportedly involved in media influence operations connected to Qatar, where staff in the Prime Minister’s Office were indirectly funded to shape media narratives. These operations were intended to highlight Qatar’s role in negotiations with Hamas while diminishing Egypt’s influence. Although Braverman has not been officially charged, he was likely aware of these activities due to his senior position.

Additionally, Braverman has been accused of attempting to alter official records regarding Netanyahu’s response to the October 7, 2023 attack. The official timeline was reportedly changed to make it appear that the Prime Minister issued instructions earlier than he actually did, potentially obscuring the true sequence of events during the crisis.

Despite these controversies, Braverman was recently appointed Israel’s ambassador to Britain, demonstrating continued trust from Netanyahu. This aligns with a pattern in which aides implicated in scandals are moved abroad to reduce scrutiny, rather than face consequences. The current phone hack represents another security lapse connected to Braverman, highlighting the risks posed by improperly secured communications among top officials.

The exposure of Unit 730 agents, alongside Braverman’s controversial history, underscores the seriousness of this cyber breach. It is a reminder that even senior figures with long-standing access to sensitive information can make mistakes that threaten national security.
T U Deshmukh
T U Deshmukh
T U Deshmukh is the leading voice on the subject of Jobs, AI, Data and layoffs and she regularly contributes a column on Jobs for Newsinterpretation.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
