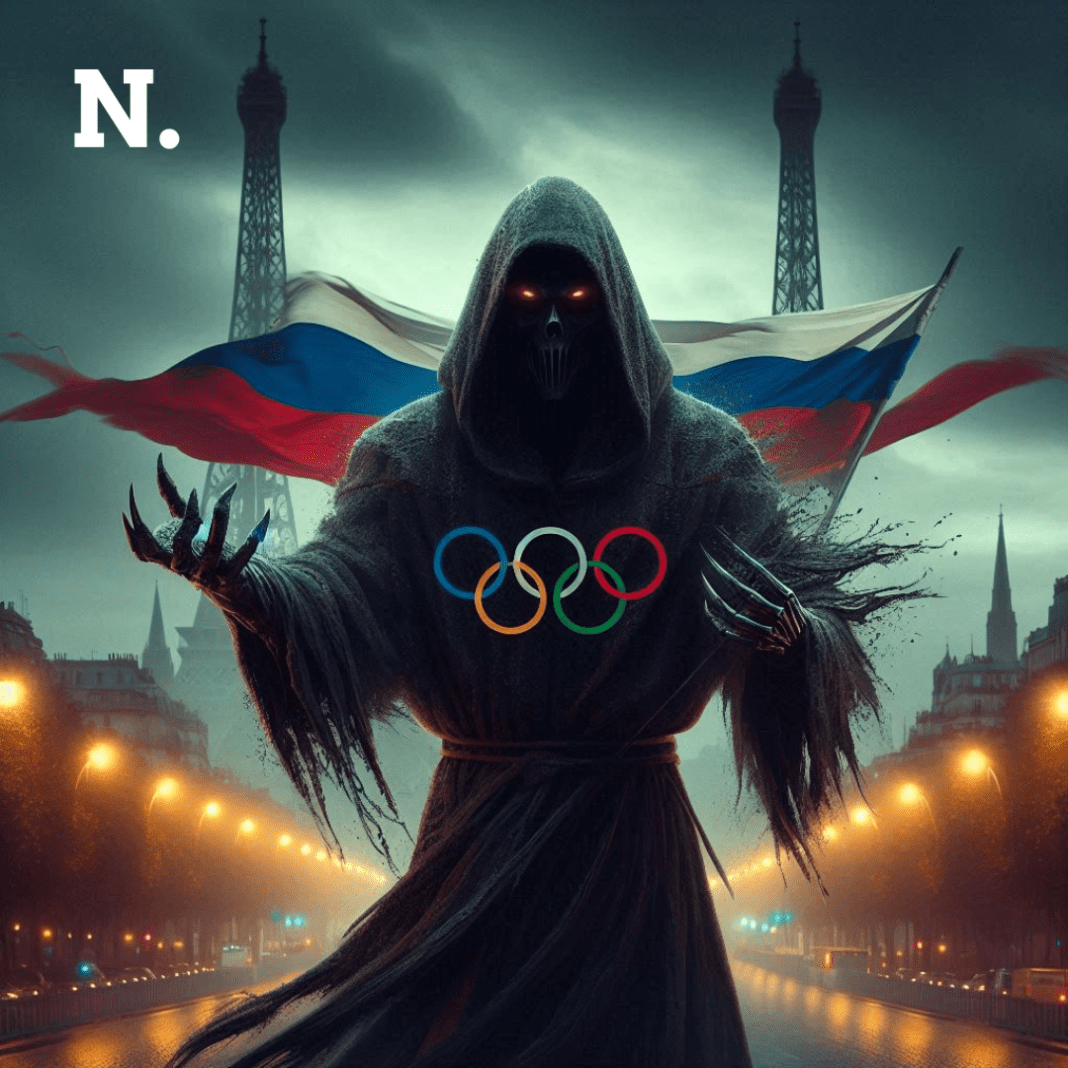
Russia was barred from the 2024 Olympics for invading Ukraine. It is said to have started a clandestine influence operation. The goal is to malign the Games and stoke anti-terrorist sentiment. These initiatives have been revealed by a recent report from Microsoft’s threat intelligence section. This report tracks the actions of those it refers to as “prolific Russian influence actors.”
The Campaign’s Objectives towards Olympics
The primary goals of this campaign are twofold: to tarnish the reputation of the International Olympic Committee (IOC) and to foster a sense of impending violence at the Paris Olympics. This aligns with Russia’s historical tactics of undermining the Olympics when it is unable to participate or win, as observed in previous decades.
Key Findings of the Report
The report reveals that the Russian campaign began targeting the 2024 Olympic Games and French President Emmanuel Macron last summer. Among the methods used was the creation of a fake documentary featuring a deepfake of actor Tom Cruise. This bogus film, titled “Olympics Has Fallen,” was designed to mimic a Netflix production and included AI-generated audio to replicate Cruise’s voice. The documentary falsely implied Cruise’s involvement and even featured sham five-star reviews from prominent news outlets such as The New York Times, The Washington Post, and the BBC.
Despite YouTube removing the documentary at the request of the IOC, it remains available on Telegram. The IOC issued a statement last fall acknowledging the wave of fake news targeting the committee, including the defamatory documentary.
Exploiting Global Tensions over Paris Olympics
The report highlights how the Russian campaign has sought to exploit existing global tensions to further its objectives. Most recently, it has capitalized on the Israel-Hamas war by impersonating militants and fabricating threats against Israelis planning to attend the 2024 Games. Some of these fabrications referenced the 1972 Munich Olympics attacks, where members of the Israeli Olympic team and a West German police officer were killed by an affiliate of the Palestine Liberation Organization.
Tactics and Methods used to tarnish Paris Olympics
Apart from the fictitious documentary, the campaign has used films that mimic news sources. These films make plausible threats of violence during the Paris Games.
In one such video, which claimed to be from Brussels’ Euronews, it was erroneously said that Parisians were purchasing home insurance in case of terrorist attacks.
Another fake news item purported to be from French station France 24. It said, incorrectly, that tickets to 24 percent of Olympic events had been returned because of concerns about terrorism.
A third attempt featured a fictitious press release on video. It purported to be from the French intelligence chief and the CIA. This video alerted viewers to potential terror risks during the 2024 Olympics.
Historical Context and Comparisons
Microsoft’s analysis notes that the present campaign and previous Soviet efforts have a history of attacking the Olympics. It draws comparisons between the two. For example, the Soviet Union boycotted the 1984 Summer Olympics in Los Angeles. They tried to induce other nations to follow suit. They did this by secretly distributing flyers. These flyers alerted nonwhite athletes of the threat of violence from radical Americans.
Once it was discovered that Russian athletes were widely using performance-enhancing substances, the IOC banned Russia from the 2018 Winter Games in 2017. Russia and Belarus’s allies are therefore restricted to competing in the 2024 Summer Olympics as “individual neutral athletes,” meaning that they cannot fly their national flags.
Recent Developments and Responses
Microsoft claims that the internet influence effort picked up steam soon after the IOC’s suspension decision. The study’s director, retired FBI agent Clint Watts, pointed out that Russia has updated its outdated playbook for the Paris Games with new generative AI techniques in an attempt to dissuade viewers from going out of fear of physical violence.
Despite these efforts, the International Olympic Committee remains vigilant, actively combating misinformation and disinformation campaigns targeting the Games. The Russian Embassy, when approached for comment, did not immediately respond.
Conclusion
Russia’s clandestine influence campaign against the 2024 Paris Olympics underscores persistent geopolitical tensions. It shows the lengths to which state actors may go to achieve their objectives. By employing advanced technologies such as AI and deepfakes, Russia has sought to undermine the IOC’s credibility. They aim to instill fear among potential attendees. As international bodies navigate these challenges, robust cybersecurity becomes critical. Media literacy is also essential in safeguarding the integrity of global events.