

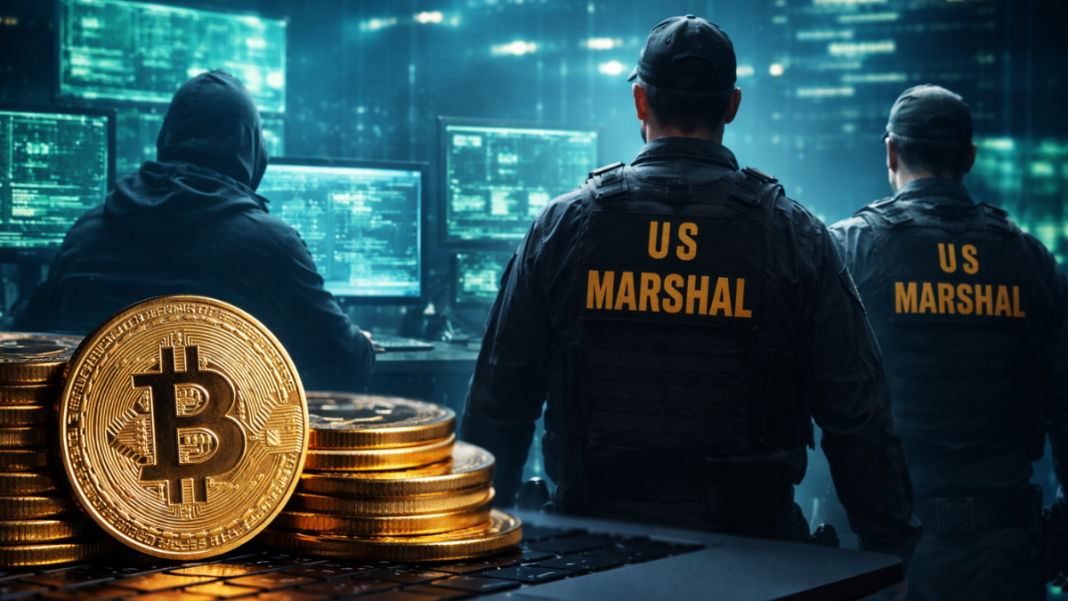
US Marshals investigate potential hack of government-controlled cryptocurrency wallets

The US Marshals Service has confirmed that it is investigating a possible cyber incident involving digital assets controlled by the US government. These assets mainly include cryptocurrencies that were seized or forfeited during criminal and civil law enforcement actions and are held in official government-managed digital wallets. Because the agency acts as the custodian of these assets, any suspected security issue is treated as a high-priority matter.

The issue gained wider attention after online discussions suggested that government-linked digital wallets may have been affected in a large crypto theft. While officials have not confirmed the extent of the issue, they have stated that the matter is under active investigation and that no additional details will be released at this stage. This approach is common when cybersecurity cases involve sensitive financial systems and public assets.

Government-Controlled Digital Assets and the Investigation

The US Marshals Service is responsible for holding and safeguarding cryptocurrencies that are seized by federal agencies during investigations or forfeited through court proceedings. These digital assets are not owned for investment purposes. Instead, they are held securely until legal processes are completed or further government action is taken.

Cybercrime group Everest says it stole nearly 900GB of Nissan data in major attack

Digital assets are stored in online wallets that rely on cryptographic security, meaning access is controlled through private digital keys. If these keys are exposed or misused, unauthorized transfers can occur. Because of this, strong digital security is essential, especially when large sums of money are involved.

The investigation follows public online claims that some government seizure wallets may have been connected to a broader crypto theft in late 2025. These claims were shared by an on-chain investigator known as ZachXBT, who alleged that more than $60 million worth of digital assets had been stolen across several wallets. These claims are now part of what authorities are reviewing.

Adding to the public discussion, Patrick Witt, executive director of the President’s Council of Advisors for Digital Assets, acknowledged awareness of the issue through a social media post. While no confirmation was given, his response signaled that the matter had reached senior advisory levels within the digital-asset policy space.

Why This Case Is Drawing National Attention

This possible hack has drawn national attention because it raises concerns about how the US government manages and protects digital assets held by law enforcement. The US Marshals play a key role in this system, as they are responsible for the custody and security of cryptocurrencies seized through criminal and civil proceedings.

Last year, President Donald Trump authorized the creation of a national strategic Bitcoin reserve to hold forfeited Bitcoin, along with a broader US Digital Asset Stockpile for other seized digital assets. The US Marshals are tasked with managing and safeguarding these holdings, making any questions about their security a matter of national importance.

Project Veritas drops Epstein nuke — DOJ distances itself as claims of Trump cover-up go viral

Because these reserves can hold assets worth millions of dollars, they are considered high-value targets. This places added responsibility on the US Marshals, as any weakness in custody systems could expose public assets to risk. Unlike traditional bank accounts, cryptocurrency transactions cannot be reversed once completed. This means that even a single successful breach could lead to permanent losses, increasing the seriousness of any suspected incident involving wallets managed by the US Marshals.

Major news organizations such as Reuters and Bloomberg News have reported on the investigation, reflecting its national importance and the broader concern about digital-asset security and the role of the US Marshals in protecting seized assets.
Crypto Crime and the Wider Context

The probe involving the US Marshals comes at a time of rising cryptocurrency crime worldwide, as cybercriminals increasingly target digital wallets, exchanges, and storage systems, including those used by government agencies.

US imposes sanctions on 6 Gaza charities and a Palestinian group over alleged
Hamas links

Research published by Chainalysis shows that more than $3.4 billion worth of cryptocurrency was stolen globally in 2025, affecting individuals, private companies, and institutions. This broader trend has added urgency to investigations being conducted by the US Marshals.

Although blockchain transactions are publicly visible, theft remains possible through malware, stolen credentials, or technical weaknesses. The investigation highlights the challenges faced by the US Marshals in securing digital assets and ensuring that government-held cryptocurrencies remain protected.

Samruddhi Kulkarni
Samruddhi Kulkarni
Samruddhi Kulkarni is a cybersecurity and artificial intelligence specialist who reports on emerging cyber threats, advanced AI systems, and data-driven risk trends shaping the digital world.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
