Introduction to the Yi Peng 3 Incident
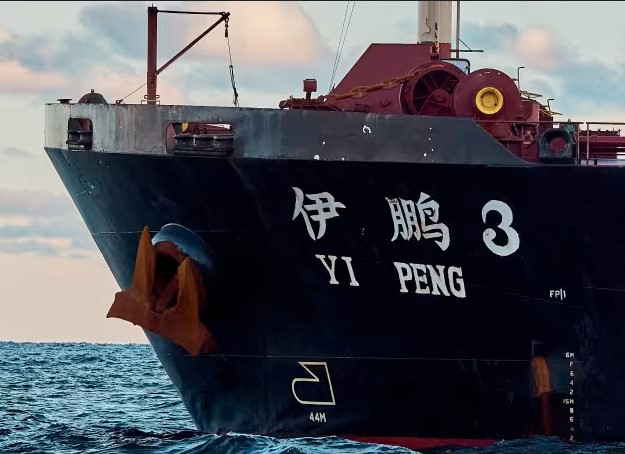
European warships have surrounded the Chinese commercial vessel, the Yi Peng 3, in international waters for over a week, placing it at the center of a significant international investigation. This investigation stems from a suspected sabotage that threatens to escalate tensions between Beijing and European countries. The ship, which is 225 meters long and 32 meters wide, was carrying Russian fertilizer when it became the focus of authorities.
The suspicion centers around whether the Yi Peng 3 deliberately severed two critical undersea cables while it was in Swedish waters. The cables are essential for internet communication between European countries. Authorities suspect that the incident may not have been accidental, as investigators believe the ship’s anchor, dragging along the seabed for over 100 miles, may have caused the damage to the cables.
The Investigation and Suspected Sabotage of Yi Peng 3
The Yi Peng 3 left the Russian Baltic port of Ust-Luga on November 15 and sailed toward its destination. During the voyage, its anchor became dislodged, dragging along the seabed. The anchor is thought to have severed two crucial data cables, one connecting Sweden to Lithuania and the other connecting Germany and Finland, on November 17 and 18. This led to a significant disruption in communications across the region.
Investigators are now looking into whether the ship’s captain was intentionally involved in sabotaging the cables. They suspect that Russian intelligence agencies might have played a role in directing the attack. The captain of the vessel, who is Chinese, was likely aware of the dragging anchor as it reduced the ship’s speed for hours. Despite this, the ship continued its journey and cut through the cables.
The ship’s transponder, a device that tracks its movements, was turned off during the time the cables were damaged. This is what investigators call a “dark incident,” where the ship’s location becomes unknown, raising further suspicion. Danish Navy ships pursued the ship, which finally came to a stop in the Kattegat Strait, connecting the Baltic Sea to the North Sea.
Legal and Political Complications
The situation is complicated by the legal rules governing international waters. According to maritime law, European countries like Denmark, Sweden, and Germany cannot force a foreign ship to dock in their ports without solid legal reasons. Despite this, European authorities are determined to investigate how the Yi Peng 3 caused the damage. Sweden has opened a sabotage investigation into the cables. Both Swedish and German authorities are working together to gather evidence. They are trying to speak with the ship’s crew. However, this has proven difficult since the ship remains in international waters.
The Chinese shipping company that owns the Yi Peng 3, Ningbo Yipeng Shipping, has been cooperating with the investigation. However, the company has not made any public statements regarding the incident. The ship’s presence in international waters, guarded by warships from NATO countries, creates a delicate situation. While European nations closely monitor the ship, they must tread carefully to ensure they do not violate their commitment to freedom of navigation in international waters.
The situation also highlights the increasing tensions between Russia and the West, particularly since the ongoing war in Ukraine. European officials have accused Russia of orchestrating attacks on critical infrastructure, including undersea pipelines and data cables. The sabotage of undersea cables has been a recurring issue, and this latest incident involving the Yi Peng 3 only adds fuel to the fire.
The Bigger Picture and Past Incidents
The damage caused by the Yi Peng 3 is not an isolated case. In October 2023, another Chinese-registered vessel, the Newnew Polar Bear, severed a gas pipeline and a communication cable in the Baltic Sea during a similar incident. During that incident, Russian sailors were reportedly on board the ship. Although the authorities in Sweden, Denmark, and Norway did not stop the ship due to a lack of clear legal justification, the event raised concerns about the role of Russian interests in such incidents.
The latest event with the Yi Peng 3 is significant due to the vessel’s route. After years of operating only in Chinese waters, the ship changed its course in March 2024 to include Russian ports. This shift is under scrutiny by investigators as it may provide clues about potential Russian involvement in the incident. While there is no direct evidence linking Russia to the sabotage, the change in the ship’s operating region has raised questions.
European authorities continue their investigation into the incident. They must balance upholding international law with protecting vital infrastructure from sabotage. The damage to the cables has disrupted communication. It has also raised concerns about the security of undersea networks that connect continents. The Yi Peng 3 incident serves as a reminder of the vulnerabilities in global trade and communication systems.
The Yi Peng 3 incident has sparked significant international concern. With European warships guarding the vessel and investigations underway, the event raises important questions about maritime law, international security, and the role of foreign vessels in global infrastructure.