

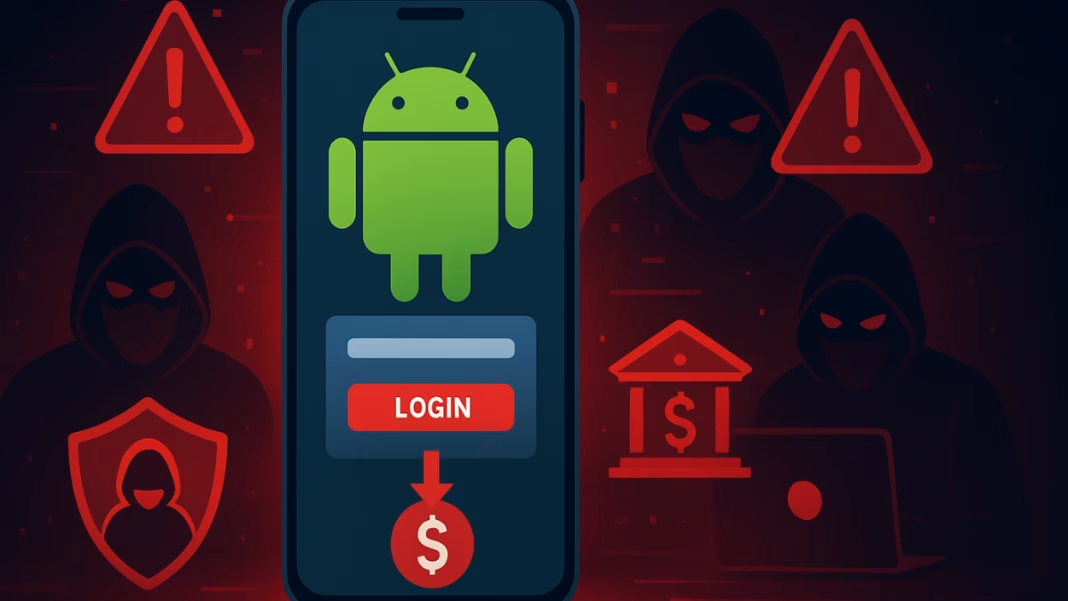
🚨 Malware nightmare: cloned banking apps rob Android users of cash and data

A new wave of dangerous malware is targeting Android phone users in India. This attack is disguised as real banking applications but is actually designed to steal money and personal data. Security researchers discovered the campaign in late July and warned that it is highly advanced and dangerous.

Malware Campaign Disguised as Banking Apps

The fake apps are made to look like real ones that people use for online banking. They copy the design and features so closely that most people cannot tell the difference. This makes it easy for the malware to trick users into installing it on their phones.

Once installed, the malware can completely take over the device. It can read personal information, watch what the user is doing, and even send or receive messages. It is also capable of carrying out money transfers without the phone owner’s knowledge.

With the rising use of mobile banking in India, millions of people could be at risk if they fall for these fake apps. Even though the report does not mention the names of the banks being targeted, experts say the threat is real for anyone using mobile banking on Android phones.

How the Attack Works

The attack starts when users receive a message on WhatsApp, SMS, or email. The message may contain a link to download an app or a QR code to scan. These apps come in APK file format, which can be installed manually on an Android phone.

The messages are designed to look like they are from trusted sources. They might say the app is a system update or an official banking app. Some attackers also use fake app stores that look like the Google Play Store to make the download look safe.

How Cyber Attacks on Industrial Control Systems Can Endanger Lives ?

When the user installs the fake app, it asks for a wide range of permissions. These permissions allow the malware to read text messages, send messages, and access phone calls. This gives it the ability to read one-time passwords (OTPs) sent by banks for transactions.

The malware does not stop there. It bypasses Android’s battery-saving settings so it can keep running in the background. Even if the phone is restarted, the malware stays active. It can also hide or change notifications so the victim does not see any alerts from the bank or the phone company.

All the information collected—such as passwords, tokens, and OTPs—is sent to a database controlled by the hackers. This gives them full access to the victim’s bank account and other sensitive accounts linked to the phone.

Why This Malware Is So Hard to Detect

One of the most dangerous parts of this malware campaign is how quietly it operates. By hiding notifications and bypassing normal system restrictions, it avoids raising suspicion. The victim often does not realize anything is wrong until money has already been stolen.

Most people are used to trusting mobile apps, especially if they look professional. Attackers take advantage of this trust by creating apps that are almost identical to real banking apps. The design, logo, and layout are copied to trick users into thinking the app is genuine.

Cyberattack Catastrophe: How Hackers Can Endanger Human Lives ?

Many apps, even safe ones, request more permissions than they truly need. This makes it harder for people to notice when an app is asking for dangerous access. For example, if a banking app asks for permission to read SMS messages, users might think it is normal for OTP verification. But in the hands of malware, this access can be used to steal account codes and drain money.

Security experts say the only safe way to install apps is through official sources like the Google Play Store. People should be cautious about clicking links in messages or scanning QR codes from unknown senders. Reviewing permission requests carefully before installing an app can also help prevent attacks like this.

This campaign is a reminder that mobile phones are now targets for serious cybercrime. The same devices people use for social media and chatting are also where they keep banking apps and sensitive information. Criminals know this—and they are creating increasingly clever ways to take advantage of it.
Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
