

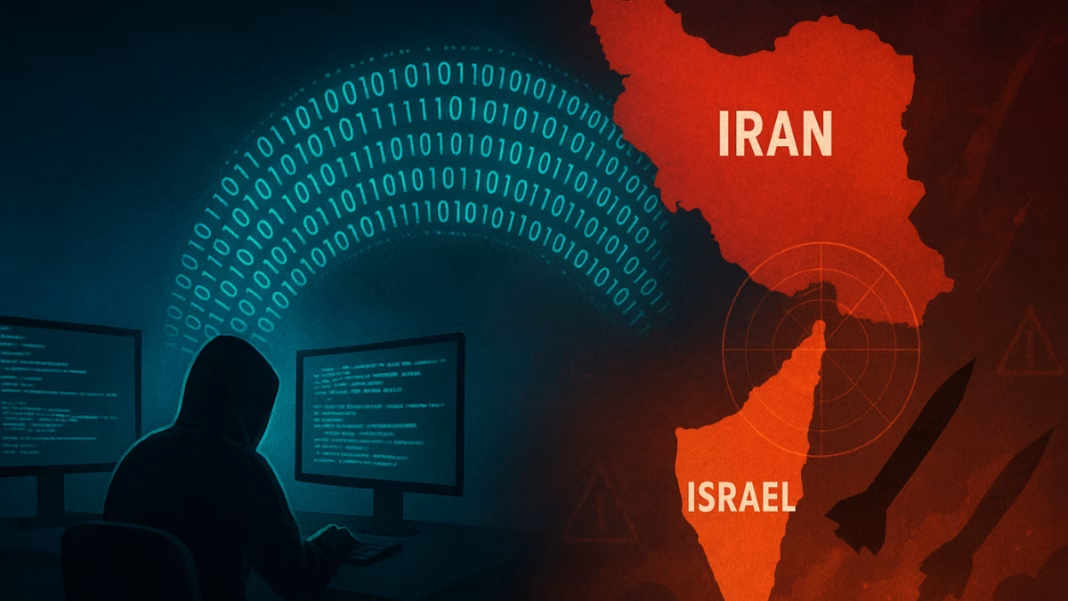
$90 million stolen, banks crippled, air defenses hacked —Iran and Israel locked in shadow war

The guns may have fallen silent between Iran and Israel, but their war has not truly ended. Instead, the battlefield has moved online. A decade-long cyber conflict between the two nations has intensified in recent months, despite a ceasefire on the ground.

During and after the 12-day war in June, cyberattacks surged. Both sides have been accused of carrying out hacks, data breaches, and digital sabotage. Officials confirm that even though no physical fighting is happening, the cyber war is still active and aggressive.

Ceasefire in Reality, But Digital Attacks Never Stopped

In the real world, a fragile ceasefire remains in place. But in cyberspace, there are no pauses. Attacks from both sides continue without interruption.

Soon after the June fighting began, Israeli officials reported receiving suspicious text messages. These messages contained dangerous links meant to steal information. At the same time, Iranian officials said their country faced more than 20,000 cyberattacks during the 12-day war.

One of the most damaging attacks targeted Iran’s air defense systems on June 13. This happened just as Israeli jets launched an air strike on Tehran. The attack was described as highly tactical and aimed at giving Israel a strategic edge. Experts say it also helped gather critical intelligence on Iranian military leaders and nuclear scientists.

Iranian-linked hackers have also stayed active. They have used weaknesses in popular software to try and break into Israeli systems. Many of these attacks focus on stealing data, spreading false messages, or disrupting important services.

Major Cyber Hits on Banks, Crypto Exchanges, and Companies

Both sides have been accused of targeting financial and business systems. One hacking group linked to Israel reportedly stole around $90 million from an Iranian cryptocurrency exchange. The stolen funds were moved to a digital wallet that had no private access keys, making it impossible for the exchange to recover the money.

The same group also attacked two major Iranian banks. These included a state-affiliated bank. The hackers disabled the banks’ main systems, backups, and even their disaster recovery networks. A software provider for the banks confirmed the damage.

Belarusian hackers destroy Aeroflot servers, steal 22 terabytes of data in targeted cyber operation

On the Iranian side, hackers carried out attacks on around 50 Israeli companies. These companies were in fields like logistics, technology, and human resources. Stolen data included the resumes of thousands of Israeli citizens who had links to the defense sector.

Some cyberattacks used fake emergency alerts. Hackers sent messages that looked like they were from Israel’s Home Front Command. These messages told people to stay away from bomb shelters. In other attacks, hackers tried to break into security camera systems.
They wanted to see where rockets were hitting.

How the Cyber War Is Changing the Conflict

The cyber conflict has shown that wars no longer need to be fought only with weapons and soldiers. Hackers can cause serious damage without firing a single shot.

In Iran, cyberattacks have led to major disruptions. The loss of key data, stolen money, and attacks on critical infrastructure have forced officials to call for urgent improvements in their defenses. One weakness is Iran’s centralised data system. This means that when hackers break in, they can access a large amount of sensitive information at once.

Cyberattack Catastrophe: How Hackers Can Endanger Human Lives ?

In Israel, cyberattacks have been disruptive but less damaging. Officials say none of the Iranian-linked attacks have caused long-term harm. However, the constant attempts to hack systems, steal data, and spread misinformation show that the cyber war is far from over.

Both countries have been engaged in a shadow conflict for decades. Cyber warfare has now become one of the main tools in this ongoing struggle. Even with physical ceasefires, the digital battlefield remains active — and both sides seem prepared to keep fighting in the virtual world.

Renuka Bangale
Renuka Bangale
Renuka is a distinguished Chartered Accountant and a Certified Digital Threats Analyst from Riskpro, renowned for her expertise in cybersecurity. With a deep understanding of cybercrimes, malware, cyber warfare, and espionage, she has established herself as an authority in the field. Renuka combines her financial acumen with advanced knowledge of digital threats to provide unparalleled insights into the evolving landscape of information security. Her analytical prowess enables her to dissect complex cyber incidents, offering clarity on risks and mitigation strategies. As a key contributor to Newsinterpretation’s information security category, Renuka delivers authoritative articles that educate and inform readers about emerging threats and best practices.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
