

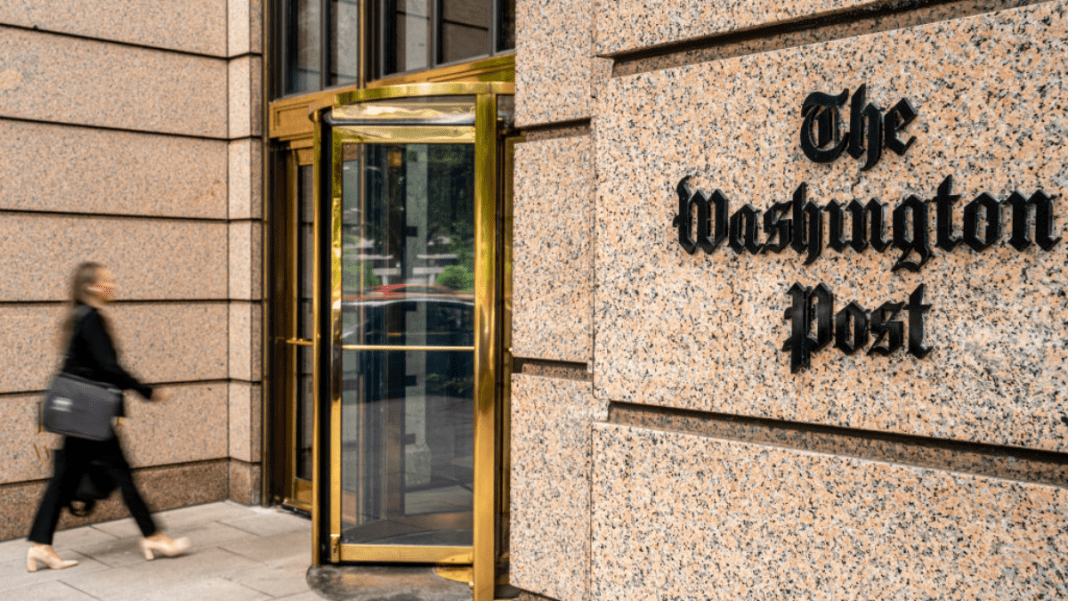
Oracle system breach exposes data of almost 10,000 Washington Post workers

The Washington Post has confirmed a serious data theft that exposed personal information belonging to 9,720 current and former employees and contractors. The data was stolen from the company’s Oracle E-Business Suite environment, which is used for important HR and financial operations.

The situation first came to light on September 29, when a “bad actor” contacted the Washington Post and claimed to have gained access to its Oracle applications. The company immediately launched an internal investigation to understand what had happened.

During the investigation, the team discovered that the attacker had been inside the company’s Oracle environment for a long period — from July 10 to August 22. This meant the attacker had weeks to quietly collect information. The breach was officially confirmed on October 27, when the company determined exactly how many people were affected and the type of data taken.

The stolen information included names, bank account numbers, routing numbers, and Social Security numbers. This type of data is extremely sensitive and can be used for identity theft or other financial crimes. The company did not provide a reason for why it took nearly a month to measure the full impact of the breach and has not answered questions about the delay.

Cyber Toufan strikes again —secret data on Iron Dome, Jericho missiles, and Australia’s Land 400 project exposed

Part of a Larger Attack Targeting Oracle Customers

The attack on the Washington Post is part of a much broader campaign targeting organizations that use Oracle E-Business Suite. The group behind the attacks is Clop, a well-known ransomware gang. Clop has been responsible for several large-scale data thefts in recent years and is known for exploiting software vulnerabilities to access company systems.

In this case, Clop took advantage of a zero-day vulnerability, now identified as CVE-2025-61882, which allowed them to break into Oracle environments without being detected. A zero-day vulnerability is a security flaw that the software maker does not know about, making it especially dangerous. Oracle released a patch to fix the flaw on October 4, after becoming aware of the issue.

Before the patch was issued, several companies had already received extortion emails from the attackers. These messages informed victims that their data had been stolen and demanded payment to prevent the data from being leaked. Cybersecurity firm Mandiant reported that Clop used multiple vulnerabilities in Oracle E-Business Suite to steal large amounts of data from various customers.

Philippines on alert as data breach fears swirl around GCash — company denies system hack

According to Cynthia Kaiser, a senior vice president at Halcyon’s ransomware research center, ransom demands in this campaign reached as high as $50 million. Clop’s data-leak site recently listed around 30 alleged victims, and the group threatened to publish stolen data from organizations that refused to pay.

Connected to Previous Large-Scale Intrusions

Clop has a long history of carrying out large attacks on widely used software systems. Their goal is usually the same: break in, steal data, and demand a large payment in return. They have successfully targeted technology vendors before, allowing them to reach and extort many downstream customers.

One of Clop’s most well-known campaigns occurred in 2023, when the group exploited vulnerabilities in MOVEit file-transfer software. That attack spread quickly because MOVEit was used by many organizations. The result was the exposure of data belonging to more than 2,300 organizations.

The recent Oracle attacks follow a similar pattern. A single flaw in widely used software created an entry point for Clop, giving them access to systems across several companies. Confirmed victims include Envoy Air and GlobalLogic, along with the Washington Post.

Organizations, researchers, and Oracle itself did not realize these attacks were happening until late September, when executives at several companies received extortion emails. Only then did the wider picture become clear, showing that many Oracle customers had been targeted in the same coordinated attack.
T U Deshmukh
T U Deshmukh
T U Deshmukh is the leading voice on the subject of Jobs, AI, Data and layoffs and she regularly contributes a column on Jobs for Newsinterpretation.

TOP 10 TRENDING ON NEWSINTERPRETATION

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

How AI Agents Are Used in Cyber Attacks: From Assisted Hacking to AI-Orchestrated Espionage

Attackers now use AI agents to scan networks, write exploits and run extortion campaigns. A research guide to documented cases, including the first reported AI-orchestrated espionage campaign, and what defenders should do.

Cyber Attacks on AI and LLMs: How Attackers Target Large Language Models

Prompt injection, data poisoning, model theft and jailbreaks: a research guide to how attackers target AI systems and large language models, with real cases and defences.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Weaponized Drones: Hijacking, GPS Spoofing and Emerging Cyber Warfare Risks

How drones can be hijacked, jammed or misled by GPS spoofing, what researchers have demonstrated, and why governments treat drone fleets as a security risk.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

Operational blunder exposes massive Russian cyber espionage attack on Ukrainian prosecutors

A major cyberattack has compromised the email accounts of...

Cyber Attacks on Space Infrastructure: Satellites, GPS and the Ground Systems Behind Them

From the Viasat KA-SAT hack to GPS jamming over the Baltic, a research guide to how attackers target satellites, navigation signals and ground stations, and why it matters on Earth.

French Supermarket Refrigeration Cyberattack: How Hacking the Cold Chain Can Endanger Lives

In October 2026 attackers heated refrigeration cabinets in hundreds of French supermarkets to as much as 50°C. No one was hurt, but the attack shows how hacking the cold chain can endanger lives through fire, food poisoning and spoiled medicines.

Cyberattacks on Nuclear Facilities: Stuxnet, Kudankulam and the Limits of Air Gaps

Stuxnet, the Davis-Besse worm and malware at India’s Kudankulam plant: what they show about cyber risk at nuclear facilities and the limits of air gaps.

Triton: When Hackers Target the Safety Systems That Prevent Industrial Disasters

The 2017 Triton attack targeted the safety systems that prevent industrial disasters. What happened, who was charged, and how plants protect their last line of defence.

Cybersecurity Risks in Smart Cities: When Connected Infrastructure Fails

How connecting traffic control, emergency alerts and utilities concentrates cyber risk in cities, what the Dallas and Atlanta incidents showed, and what governments recommend.

Ransomware Attacks on Hospitals: How Healthcare Cyberattacks Put Patients at Risk

How ransomware against hospitals and their suppliers delays care and endangers patients, what the Düsseldorf and WannaCry cases show, and what research says about deaths.

FBI warns of AVrecon malware targeting outdated routers linked to proxy based cybercrime

A serious cybersecurity warning has been issued regarding commonly...

Related Articles

Popular Categories
